Security Practitioner
SEARCH
CATEGORIES
TAGS
Your Password Policy Can Pass. Your Passwords Can Still Fail.
See Your Active Directory Passwords From an Attacker’s Perspective Join Horizon3 and Shaun Hunt, CIO of McKenney’s and a longtime NodeZero® customer, for a live conversation about Active Directory password exposure and how NodeZero AD Password Audit helps uncover credentials that could be targeted through password cracking, password spray, credential stuffing, and credential reuse.
Trading Maintenance for Momentum: Scaling Security Validation Across 230+ Sites
See how a global automotive technology manufacturer used NodeZero to reduce testing overhead, cut comparable test runtime by 50%, and scale security validation across more than 230 sites.
How Kyocera AVX Built a Global Security Validation Program from Zero
See how Kyocera AVX used NodeZero to build a global security validation program, scale autonomous pentesting across manufacturing sites, and remediate more than 30,000 vulnerabilities and misconfigurations.
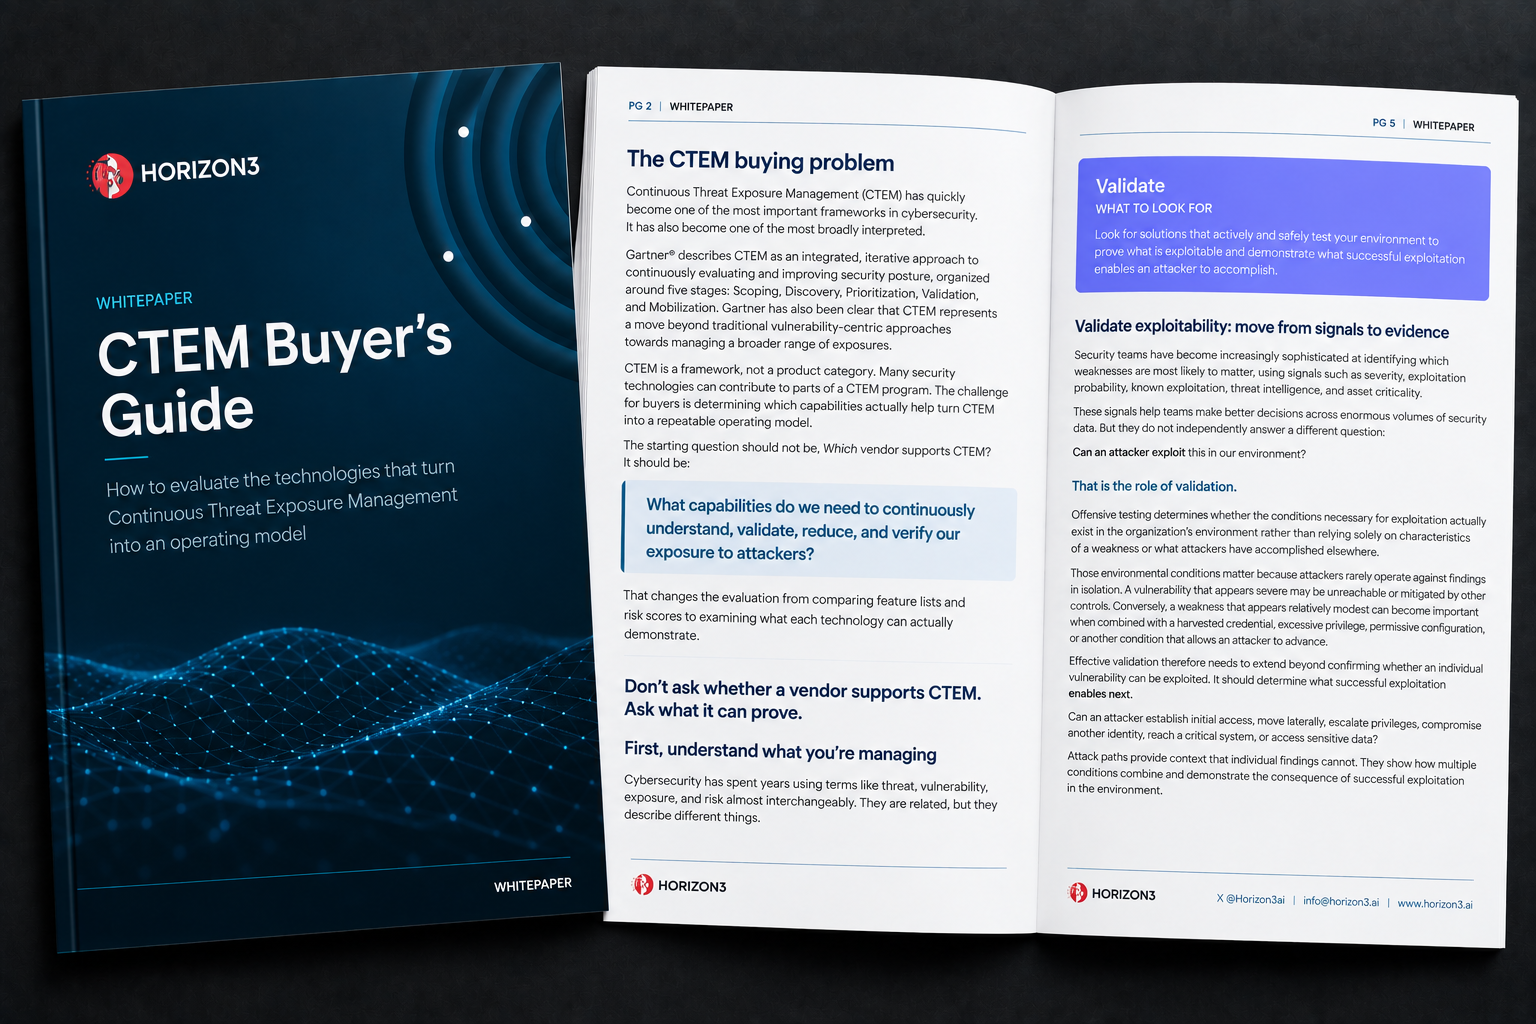
CTEM Buyer’s Guide: How to Evaluate the Technologies That Turn Continuous Threat Exposure Management Into an Operating Model
September 17, 2026
Learn how to evaluate CTEM technologies based on what they can prove, from exploitable attack paths and remediation priorities to verification and measurable risk reduction.
CTEM Technology Evaluation Scorecard
September 16, 2026
Use the CTEM Technology Evaluation Scorecard to assess technologies across the CTEM operating model, score capabilities based on demonstrated evidence, and identify critical validation and verification gaps.

CISO’s CTEM Evaluation Checklist
September 16, 2026
Use the CISO’s CTEM Evaluation Checklist to assess whether technologies supporting your CTEM program can prove exploitability, demonstrate attack impact, verify remediation, and show measurable exposure reduction.

Security Data Isn’t the Problem. Security Context Is.
September 15, 2026
Security teams don't need more data. They need context. See how Horizon3 and CrowdStrike connect validated exposure evidence with security telemetry to help teams prioritize what matters most.
Patch Tuesday to Pentest Wednesday: How an Equipment Rental Company Is Turning Continuous Testing Into Continuous Exposure Management
September 9, 2026
See how an equipment rental company moved beyond point-in-time pentesting with NodeZero®, continuously validating exploitable risk, driving remediation, and measuring whether exposure is actually decreasing.

What Fal.Con 2026 Reinforced: AI Makes Proving Exposure More Important Than Ever
September 4, 2026
AI is accelerating vulnerability discovery, but security teams still need to know which exposures actually matter. Here’s what Fal.Con 2026 reinforced about offensive security, validation, and proving risk.
How Virginia Tech Connected Pentesting to Its Engineering Workflow
See how Virginia Tech used the NodeZero GraphQL API, GitLab, and ServiceNow to automate external pentesting and create a repeatable workflow from attack validation to remediation.