Security Practitioner
SEARCH
CATEGORIES
TAGS
Which Holes Can Attackers Really Bite Into?
November 18, 2026
Security gaps can hide in unpatched systems, weak passwords, or controls that do less than expected. This infographic outlines five questions CISOs and security teams can answer with autonomous penetration testing to see what attackers can actually exploit.
Does HITL Scale? Human Oversight for Autonomous Security
Explore where human oversight improves autonomous security and where routine approval becomes a bottleneck as agent activity scales. Hear how research, NodeZero's production-safe autonomy, and HITL and HOTL models shape the decisions, staffing, and cost of operating autonomous security continuously.

Metrics That Matter: Are We Becoming Harder to Attack?
November 8, 2026
Closed tickets and remediation SLAs show what teams have done, not whether the environment is harder to attack. This infographic outlines four Exposure Management metrics: attack paths and impacts, speed of impact reduction, verification coverage, and recurrence.
From Evidence to Action: Scaling CTEM Across the Enterprise
In this webinar, Ellen Sundra, VP, Customers at Horizon3; and Dan DeCloss, Chief Customer Officer at Brinqa, will explore how unified exposure data, attacker-derived evidence, business context, and remediation orchestration can transform proof into prioritized, coordinated action.

HacktoberFest: A Fireside Chat with Horizon3 & GuidePoint Security
Continuous Validation, Real-World Risk, and Proving Security Impact Join top subject matter experts from Horizon3 and GuidePoint Security for a candid conversation on the evolving cybersecurity landscape and what organizations can do to strengthen their defenses.

CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE
October 20, 2026
Horizon3 researchers analyze CVE-2026-106173, a critical Fortinet FortiSIEM vulnerability affecting an unauthenticated gRPC service. The deep-dive explains how path traversal and null-byte handling enable arbitrary file writes and remote code execution, along with indicators of compromise for defenders.

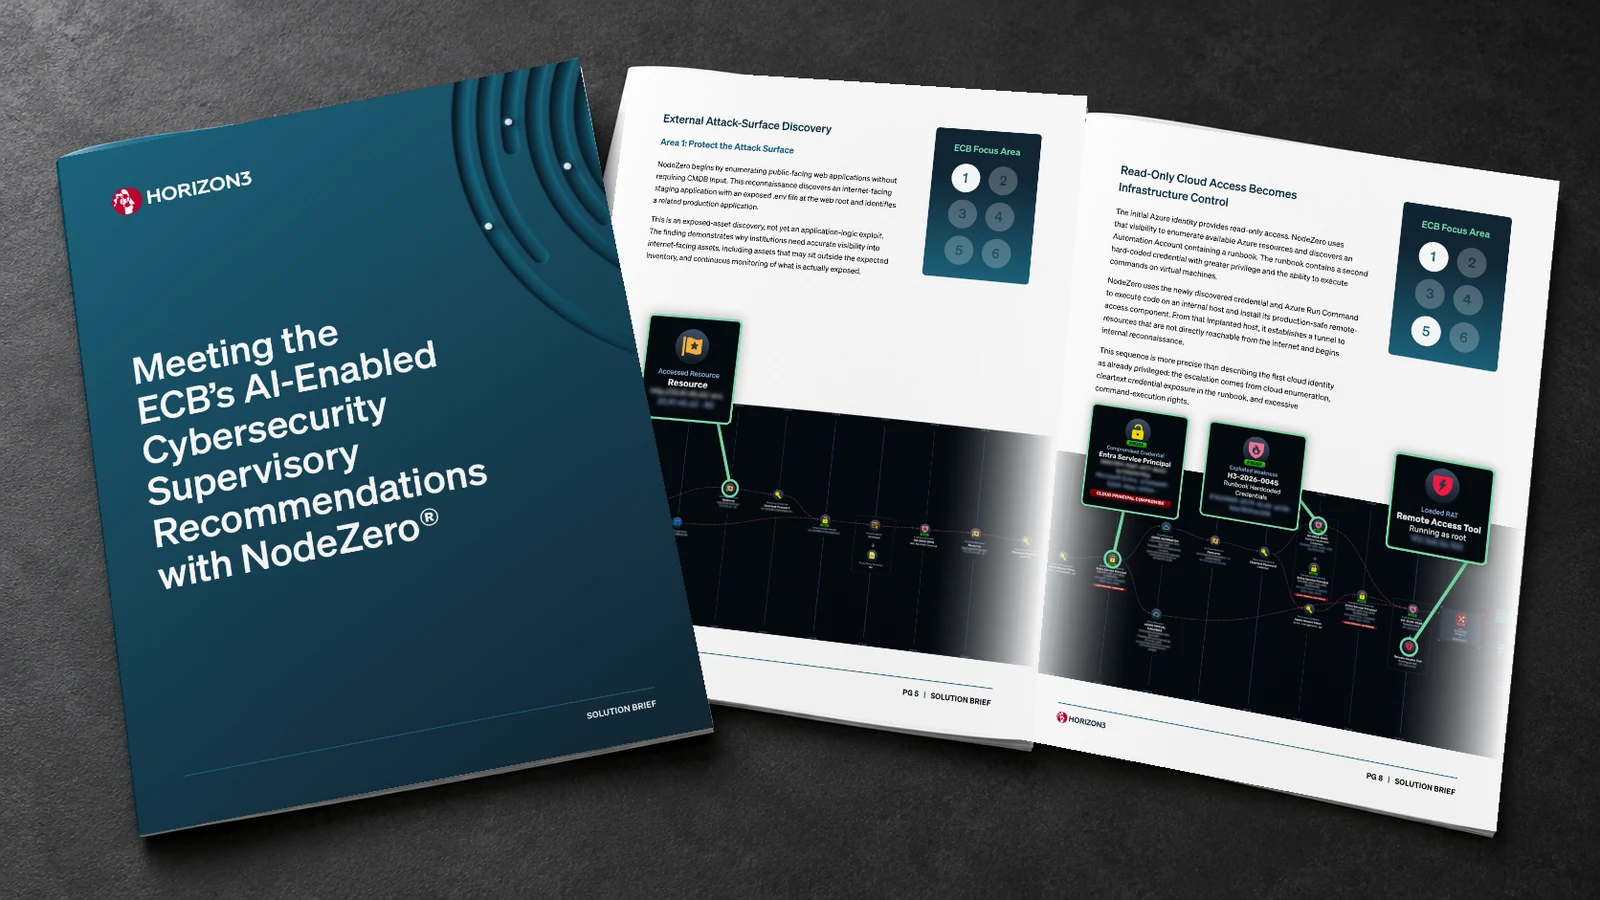
Meeting the ECB’s AI-Enabled Cybersecurity Supervisory Recommendations with NodeZero®
October 16, 2026
Explore how NodeZero autonomous penetration testing connects application, cloud, identity, and infrastructure weaknesses into validated attack paths, helping banks prioritize remediation and build evidence for the ECB’s cybersecurity supervisory recommendations.
AI Changed the Economics of Cyberattacks
October 9, 2026
AI has changed the speed, scale, and economics of cyberattacks. Learn why modern security requires continuous exposure management built around evidence, informed action, and verified outcomes.
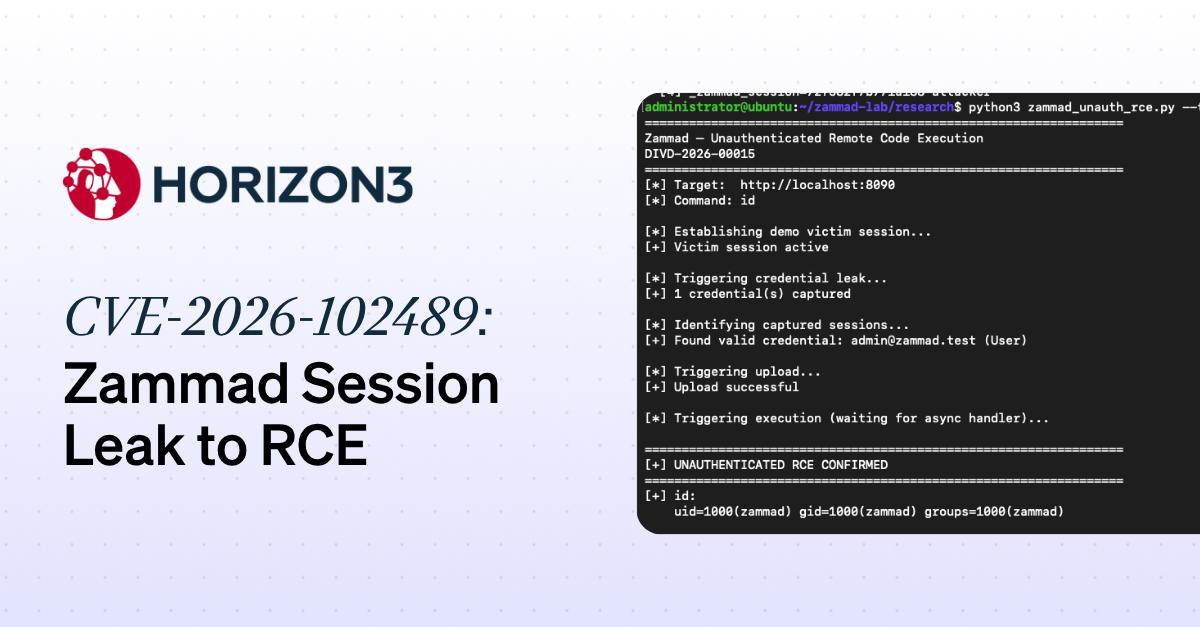
Zammad CVE-2026-102489: Session Leak to RCE
October 7, 2026
Horizon3 reverse engineered CVE-2026-102489 in Zammad, reproduced the unauthenticated WebSocket session leak, traced the vulnerable code path, and demonstrated how a leaked admin session can lead to remote code execution.
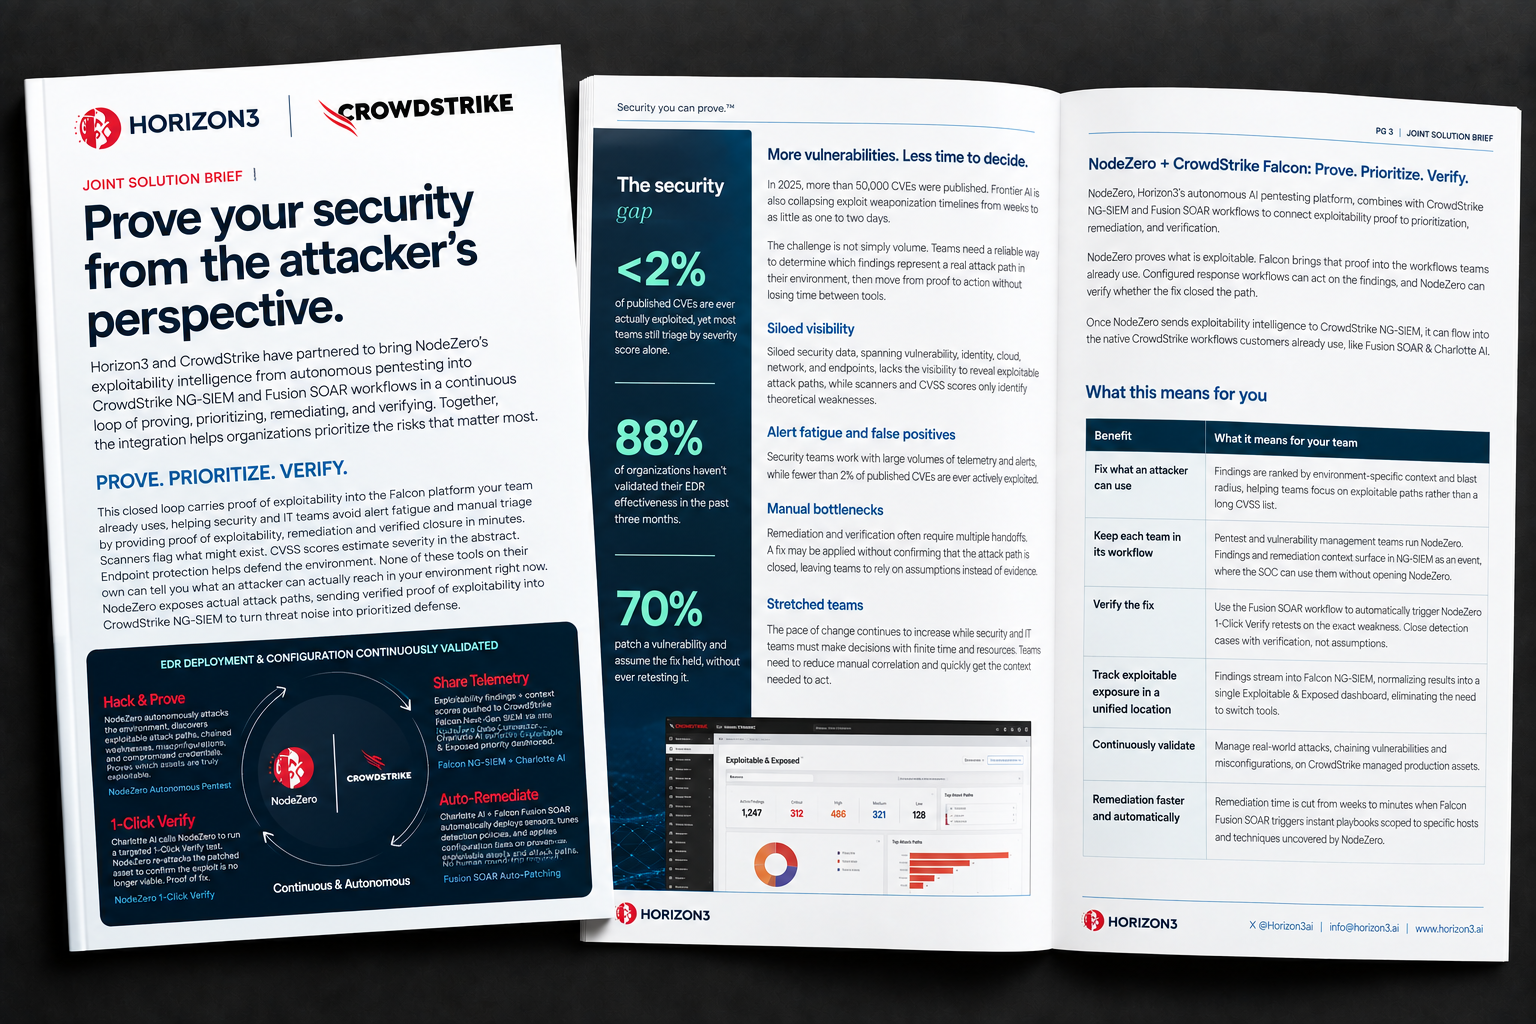
Horizon3 + CrowdStrike: Prove. Prioritize. Verify.
October 2, 2026
See how Horizon3 and CrowdStrike connect NodeZero exploitability intelligence with Falcon Next-Gen SIEM and Fusion SOAR to prove, prioritize, remediate, and verify exploitable risk.