Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-101767 is a critical (CVSS 9.8) unauthenticated SQL injection vulnerability in Oracle E-Business Suite 12.2.3–12.2.15. Horizon3 researchers identified an attack chain enabling remote code execution through the TCF servlet. Learn about affected versions, October 2026 patches, mitigations, and NodeZero Rapid Response validation.
Read More →CVE-2026-104935 is an actively exploited Ivanti Connect Secure authentication bypass that can enable remote code execution. Review the exploit chain, affected versions, fixed releases, indicators of compromise, and how NodeZero Rapid Response helps validate exposure and verify remediation.
Read More →Featured
WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
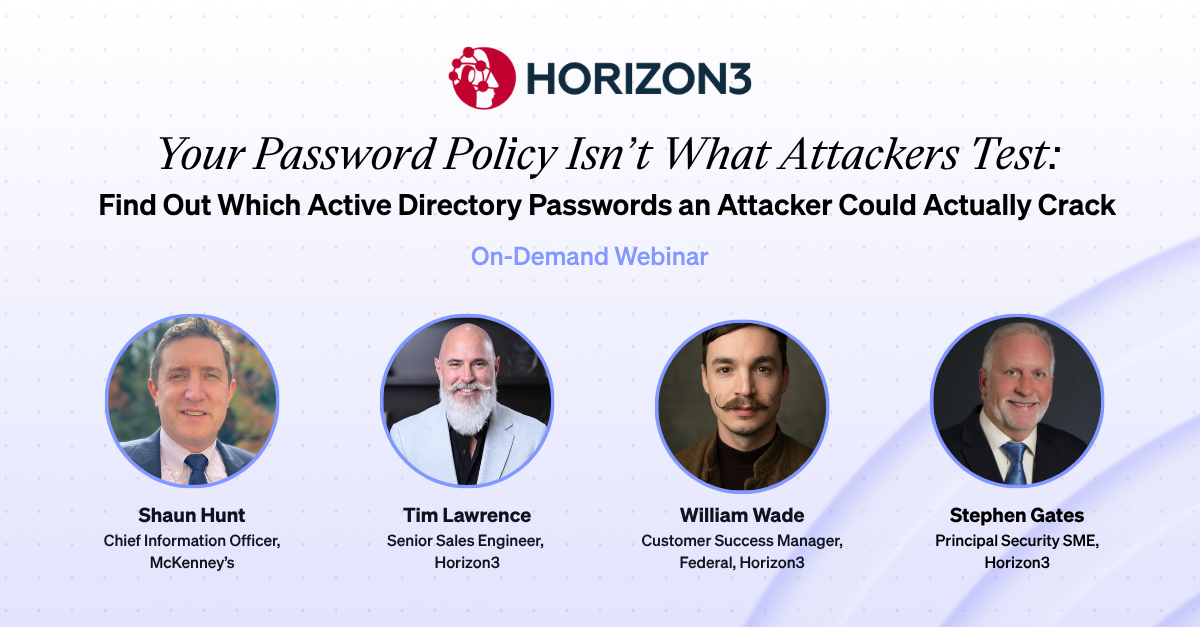
Your Password Policy Can Pass. Your Passwords Can Still Fail.
See Your Active Directory Passwords From an Attacker’s Perspective Join Horizon3 and Shaun Hunt, CIO of McKenney’s and a longtime NodeZero® customer, for a live conversation about Active Directory password exposure and how NodeZero AD Password Audit helps uncover credentials that could be targeted through password cracking, password spray, credential stuffing, and credential reuse.
CVE-2026-19490
September 28, 2026
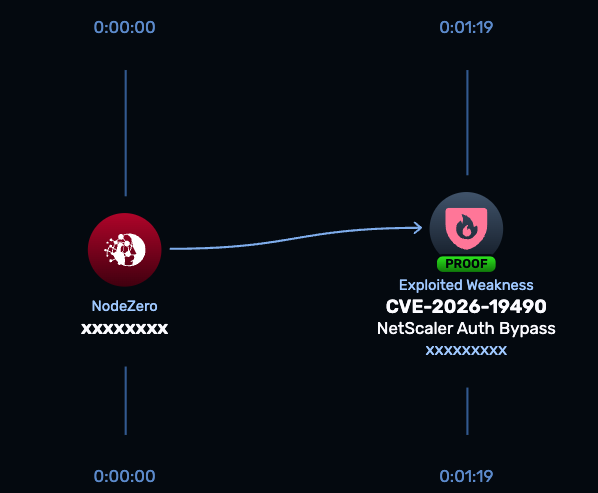
CVE-2026-19490 is a critical Citrix NetScaler ADC and Gateway authentication bypass vulnerability included in CISA’s Known Exploited Vulnerabilities catalog. NodeZero® Rapid Response safely validates exposure.
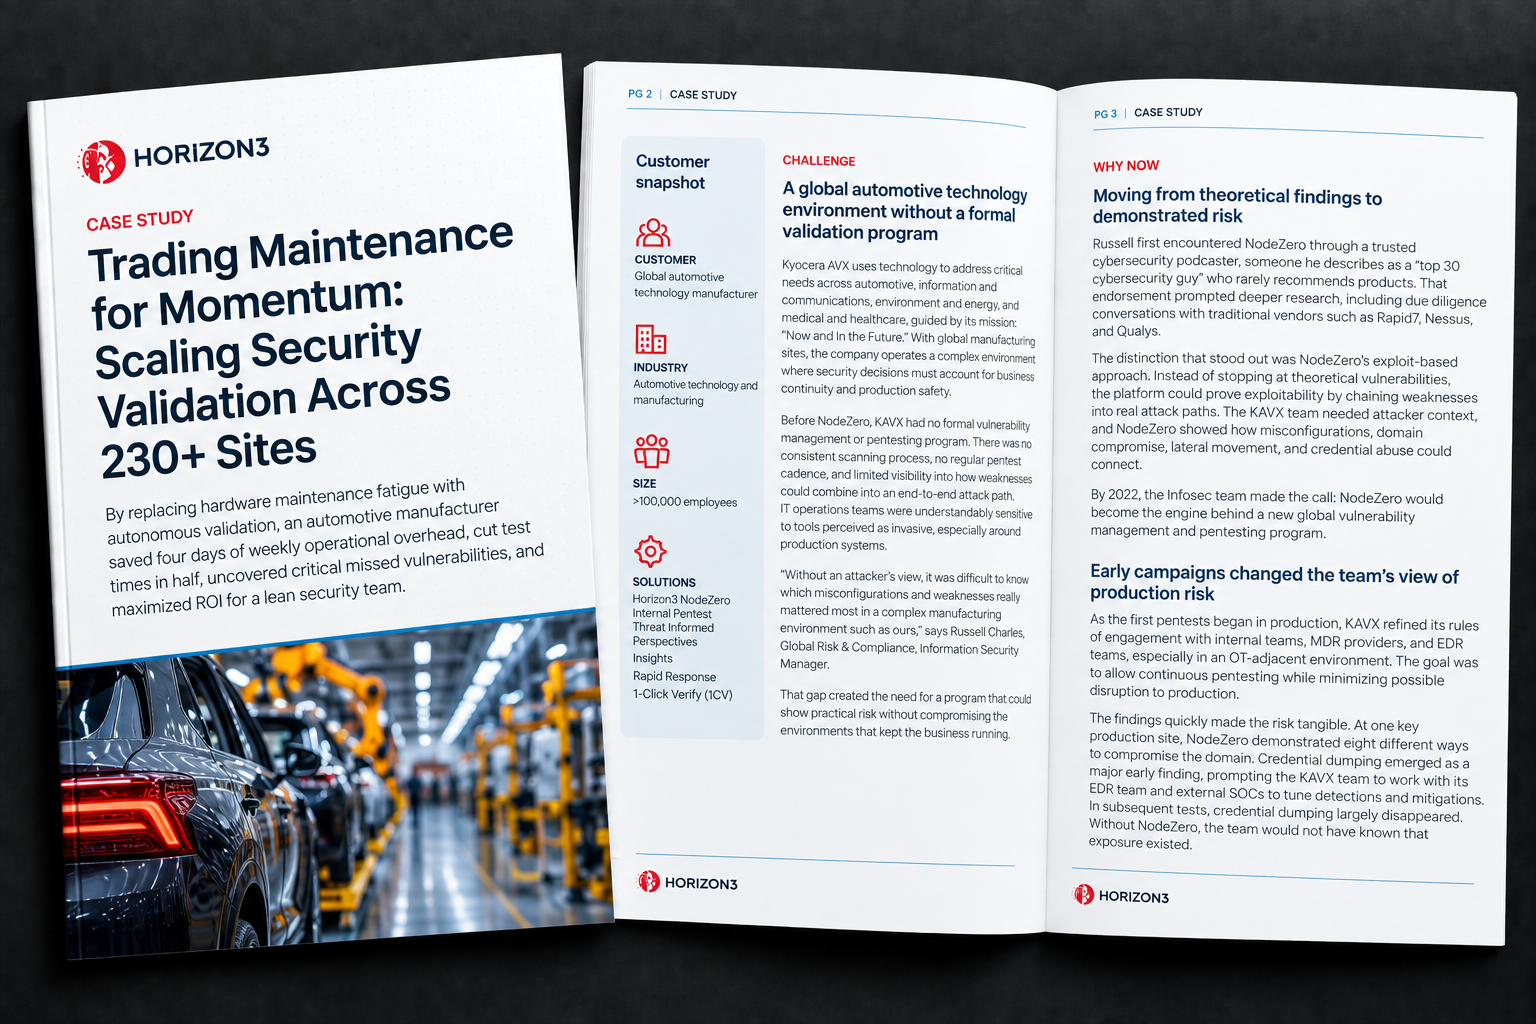
Trading Maintenance for Momentum: Scaling Security Validation Across 230+ Sites
September 25, 2026
See how a global automotive technology manufacturer used NodeZero to reduce testing overhead, cut comparable test runtime by 50%, and scale security validation across more than 230 sites.
NodeZero Federal
September 22, 2026
Horizon3's NodeZero Federal provides production-safe, autonomous penetration testing for federal agencies. Achieve continuous readiness with proven, exploitable findings and rapid retest validation.

How Kyocera AVX Built a Global Security Validation Program from Zero
September 18, 2026
See how Kyocera AVX used NodeZero to build a global security validation program, scale autonomous pentesting across manufacturing sites, and remediate more than 30,000 vulnerabilities and misconfigurations.
From Assumptions to Evidence: Why Validation Is the Heart of CTEM
In this webinar, we'll explore why validation has become one of the most important phases of CTEM, how organizations can move from assumptions to evidence, and why proof is often the difference between debating a finding and taking action.
CTEM Buyer’s Guide: How to Evaluate the Technologies That Turn Continuous Threat Exposure Management Into an Operating Model
September 17, 2026
Learn how to evaluate CTEM technologies based on what they can prove, from exploitable attack paths and remediation priorities to verification and measurable risk reduction.
CyberCom 2.0 and the Revolution in AI-Enabled Offensive Cyber Operations
September 17, 2026
AI is transforming the speed, scale, and economics of offensive cyber operations. Explore how CyberCom 2.0 can help lay the foundation for the next era of AI-enabled American cyber power.
CTEM Technology Evaluation Scorecard
September 16, 2026
Use the CTEM Technology Evaluation Scorecard to assess technologies across the CTEM operating model, score capabilities based on demonstrated evidence, and identify critical validation and verification gaps.

CISO’s CTEM Evaluation Checklist
September 16, 2026
Use the CISO’s CTEM Evaluation Checklist to assess whether technologies supporting your CTEM program can prove exploitability, demonstrate attack impact, verify remediation, and show measurable exposure reduction.
