Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
Advisory for PHP2Shell (CVE-2026-109618 and CVE-2026-109619): affected PHP versions, fixed releases, mitigations, monitoring guidance, and the NodeZero Rapid Response check.
Read More →Horizon3.ai's NodeZero Rapid Response test helps security teams validate exposure to CVE-2026-76268, a critical Splunk Enterprise vulnerability that could allow unauthenticated attackers with network access to execute operating-system commands.
Read More →Featured
WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
Integrate to Remediate Proven Attack Paths and Verify Every Fix Automatically
Discover how Horizon3 and Torq bring NodeZero® exploitability findings into SOC workflows to orchestrate remediation, contain exposed credentials, and verify that attack paths are closed.
AI Changed the Economics of Cyberattacks
October 9, 2026
AI has changed the speed, scale, and economics of cyberattacks. Learn why modern security requires continuous exposure management built around evidence, informed action, and verified outcomes.
CVE-2026-102489
October 8, 2026
CVE-2026-102489 is a critical, actively exploited Zammad vulnerability that can expose user session cookies through WebSocket errors, enabling session hijacking and potentially remote code execution.
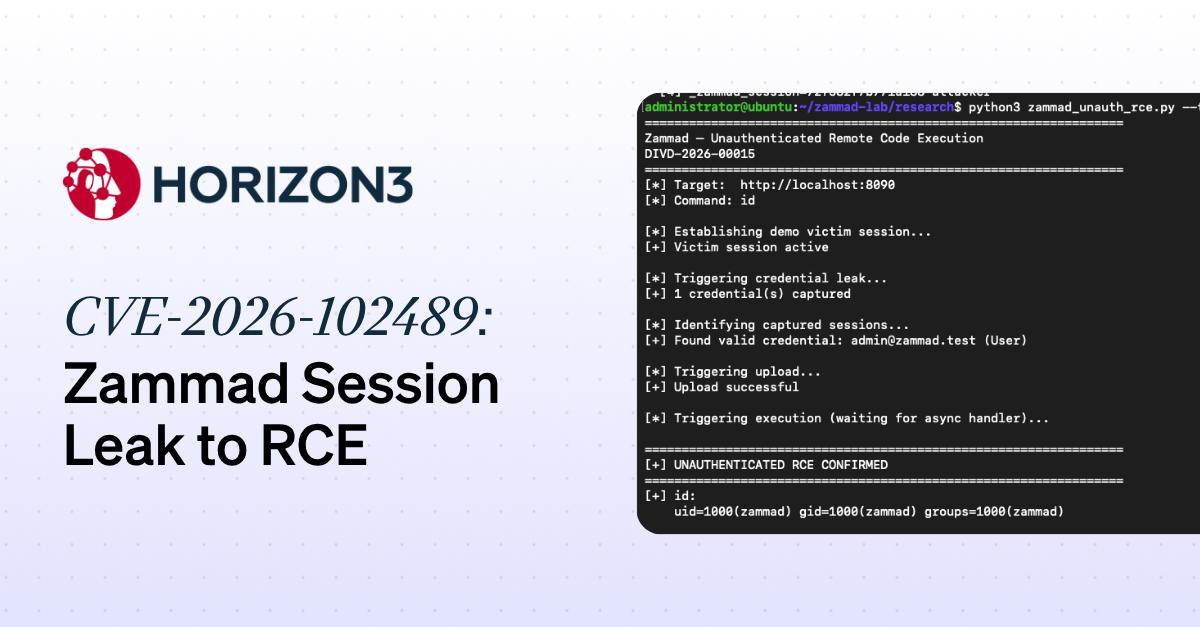
Zammad CVE-2026-102489: Session Leak to RCE
October 7, 2026
Horizon3 reverse engineered CVE-2026-102489 in Zammad, reproduced the unauthenticated WebSocket session leak, traced the vulnerable code path, and demonstrated how a leaked admin session can lead to remote code execution.
CVE-2026-21589
October 6, 2026
CVE-2026-21589 is a critical vulnerability affecting multiple Atlassian Data Center products that allows unauthenticated attackers to read specific files within the web application root. NodeZero® Rapid Response safely validates exposure.
Horizon3 + CrowdStrike: Prove. Prioritize. Verify.
October 2, 2026
See how Horizon3 and CrowdStrike connect NodeZero exploitability intelligence with Falcon Next-Gen SIEM and Fusion SOAR to prove, prioritize, remediate, and verify exploitable risk.
What Security Metrics Actually Matter?
October 1, 2026
Security activity doesn’t always equal risk reduction. Learn how attack paths, business impact, verification, remediation speed, and recurrence can show whether CTEM is actually working.
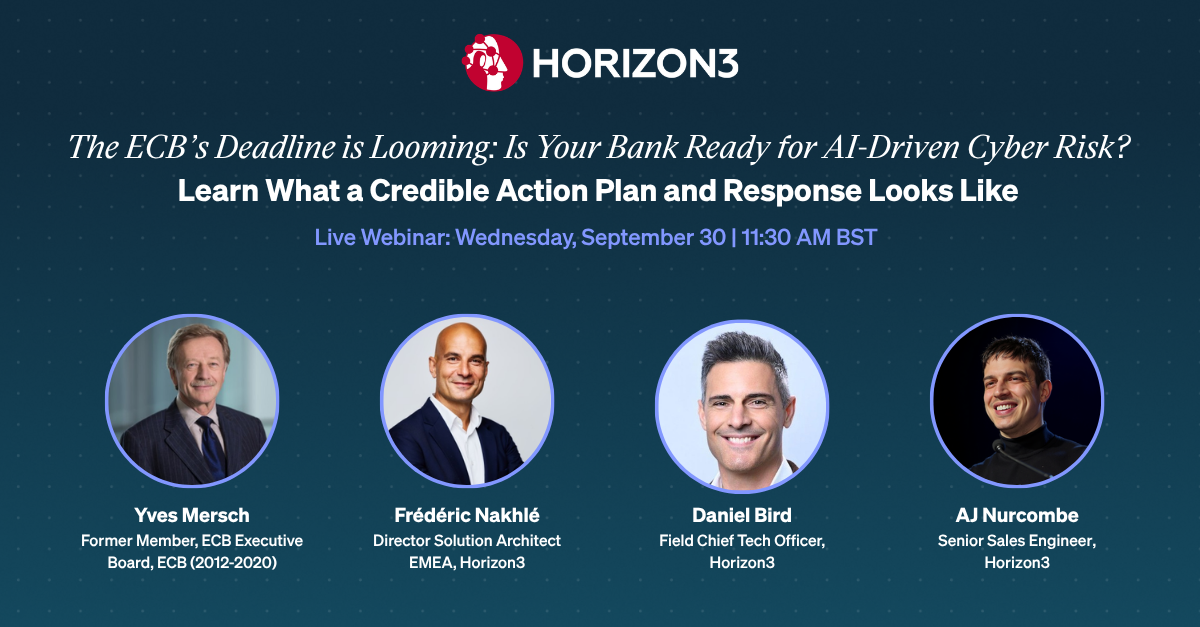
The ECB’s Deadline is Looming
Learn What a Credible Action Plan and Response Looks Like On 7 July 2026, the ECB made AI-enabled cyber risk a board-level, time-bound supervisory priority for significant institutions.With the 31 October 2026 deadline fast approaching, banks need to assess their exposure now and submit a concrete action plan to their Joint Supervisory Team. Join us…
CVE-2026-76504
September 30, 2026
CVE-2026-76504 is a critical, actively exploited Cisco Catalyst SD-WAN Manager vulnerability that allows unauthenticated API access as the admin user. Horizon3 reverse engineered the flaw, and NodeZero® Rapid Response safely validates exposure.

Horizon3’s Tales from the Trenches: Anthropic’s Mythos and Rejetto HFS
September 30, 2026
Horizon3 researchers used Anthropic’s Mythos to uncover a chain of cryptographic weaknesses in Rejetto HFS, recover a predictable signing key, forge an admin session, and achieve remote code execution.