PHP Core Remote Code Execution Vulnerabilities (PHP2Shell)
CVE-2026-109618 / CVE-2026-109619
Last updated: October 23, 2026
NodeZero Rapid Response Check Now Available
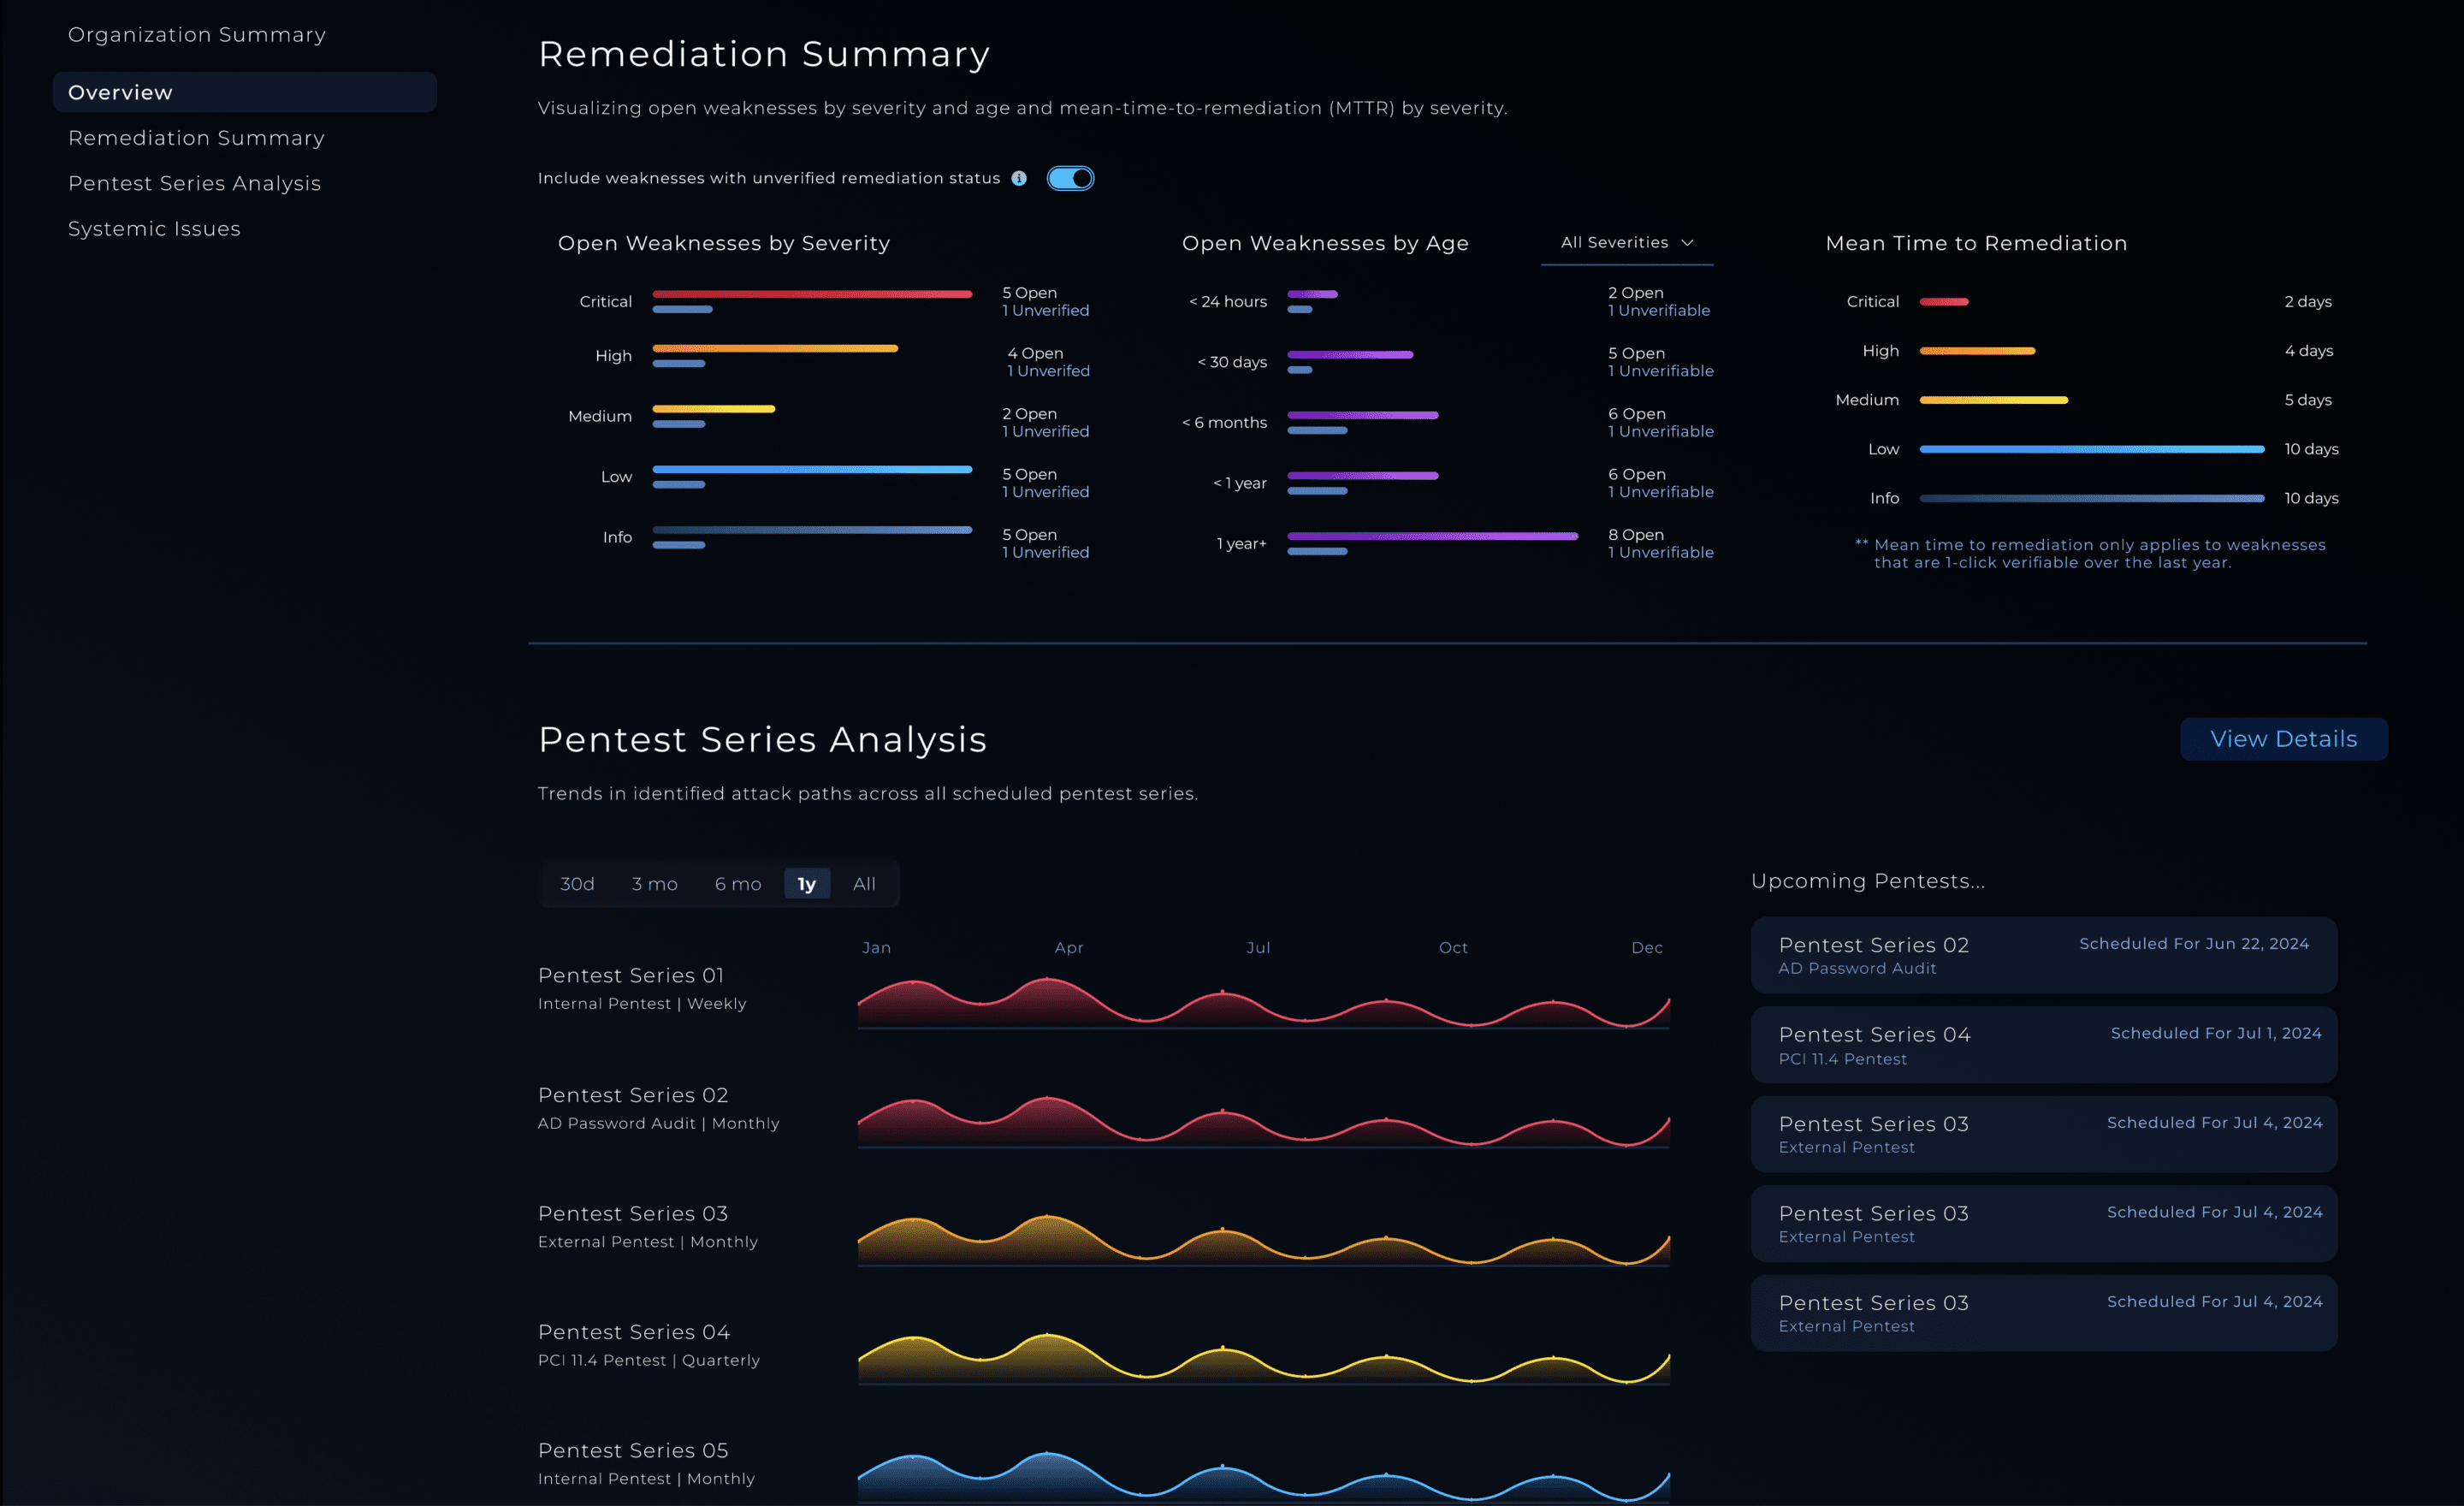
The NodeZero® Rapid Response check for PHP2Shell is now available to help identify indications of vulnerability in your environment. It combines available PHP version information with an active assessment of runtime behavior associated with the vulnerabilities. It does not attempt full remote code execution.
- Run the Rapid Response check: Launch from the NodeZero platform and review the findings and accompanying guidance.
- Patch immediately: Upgrade to a fixed PHP release or install vendor-provided packages containing the fixes. Do not delay updates while waiting for check results.
- Re-run the check: Review the result after remediation and confirm that the patched runtime is serving requests.
A negative result does not rule out vulnerability or prove that a patch is installed. Results depend on the assessed systems, configuration, and response conditions.
Use the findings to focus investigation on systems showing signs of vulnerability and support remediation decisions while patching proceeds.
Latest Updates
October 23: Additional PHP Session Upload Progress Guidance
PHP published a separate informational advisory for an unlikely RCE vector tracked as CVE-2026-115560. It recommends setting session.upload_progress.enabled=0 until the next regular bugfix release.
The issue requires an unusual combination: an application configures session.serialize_handler as php_binary or php_serialize, then changes it to php at runtime before calling session_start(), while upload progress remains enabled. Applications that never change the handler at runtime can keep the feature enabled, according to PHP.
The October 21 releases remain the fixes for CVE-2026-109618 and CVE-2026-109619. Review the additional October 23 guidance alongside those updates.
Attack Attempts Continue; Successful Exploitation Requires Separate Evidence
Recent telemetry documents scanning and exploitation attempts, including requests intended to execute commands, steal configuration data, and install persistent access. Wordfence reported no confirmed compromises in its observations as of its October 22 update. That finding is limited to its visibility and does not establish that unpatched systems are safe.
Research published on October 22 also describes successful exploitation in specific x86-64 configurations with ASLR enabled and display_errors disabled. These protections should not be treated as proof that an affected deployment cannot be exploited.
What Is Known
CVE-2026-109618 and CVE-2026-109619 are critical PHP vulnerabilities that can allow unauthenticated remote code execution. PHP released fixes on October 21, 2026.
PHP identifies all installations serving web requests as at risk, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, and LiteSpeed. The highest identified risk is associated with mod_php. Exploitation conditions vary by deployment.
CISA urges immediate patching, prioritizing internet-facing systems. Include internal applications, containers, hosted services, and products that embed PHP in your inventory.
CVSS v3.1 Scores
Red Hat’s current records list:
| Vulnerability | NVD assessment | Red Hat assessment |
| CVE-2026-109618 | 9.8 — Critical | 8.1 — High |
| CVE-2026-109619 | 8.1 — High | 8.1 — High |
For CVE-2026-109618, the assessments differ on attack complexity. CVSS measures severity, not the number of organizations or systems potentially affected.
Stop Guessing, Start Proving
Technical Details
CVE-2026-109618: Remote Code Execution via Out-of-Memory Corruption
Out-of-memory handling can interrupt PHP while internal request memory is only partially initialized. Request cleanup may subsequently process that invalid state.
PHP validated unauthenticated RCE against mod_php before application code runs. PHP-FPM prevents that particular startup-failure sequence but is considered susceptible through other conditions. The advisory reports no complete demonstrated FPM exploit for this CVE.
CVE-2026-109619: Remote Code Execution via Stale Global State
PHP workers can retain references to request-owned memory after it has been freed. A later request handled by the same worker can access that stale state.
PHP validated session lifecycle RCE against mod_php and PHP-FPM. The validated FPM path requires a suitable application operation, a fatal error, and another request reaching the same worker. Successful exploitation runs code with the web worker’s privileges.
The potential impact depends on the data, credentials, and services accessible to that account. Code execution does not automatically provide root access.
Exploitation Status
Amazon Threat Intelligence reports a PHP2Shell exploitation attempt dating to October 17, followed by additional attempts before and after disclosure. It states that it was unclear whether the pre-disclosure attempts would have succeeded against real-world systems.
Cisco Talos subsequently reported scanning and attempts to deliver payloads. Wordfence’s analysis likewise distinguishes malicious requests from confirmed compromise: establishing success requires evidence from responses or the affected server, such as process execution, filesystem changes, or outbound activity.
CISA’s October 21 statement that it had not observed exploitation describes its observations at publication. It should not be interpreted as evidence that no attempts have occurred.
Affected Versions and Patches
Supported PHP Branches
| PHP branch | Affected releases | Fixed release |
| 8.2 | Earlier than 8.2.35 | 8.2.35 |
| 8.3 | Earlier than 8.3.36 | 8.3.36 |
| 8.4 | Earlier than 8.4.27 | 8.4.27 |
| 8.5 | Earlier than 8.5.12 | 8.5.12 |
Install the applicable fixed release or distribution/LTS vendor package containing both fixes.
PHP 8.1 and older are unsupported upstream. PHP provided minimal source backports for 7.4, 8.0, and 8.1. Confirm available fixes with your provider or migrate to a supported, patched release.
Confirm the Running Deployment Is Updated
- Confirm that the fixed runtime is serving requests and restart the relevant PHP services and workers.
- Account for containers, separate PHP installations, and vendor-managed deployments.
- Obtain confirmation that a hosting provider’s update covers your application and all relevant instances.
Updating WordPress, plugins, or themes does not update PHP. Vendor backports may also retain an older PHP version number, so verify the installed package against the vendor’s advisory rather than relying solely on an HTTP version header.
Mitigations and Response
Apply the complete fixes immediately. The following measures reduce exposure to specific attack paths while updates proceed.
CISA advises organizations unable to update immediately to take PHP-based systems offline until patched or updated.
Reduce Out-of-Memory Attack Paths
For CVE-2026-109618:
- Administratively enforce
memory_limit=-1so applications cannot restore a finite limit. This removes a predictable PHP memory-limit trigger, but underlying allocation failures remain possible. - Keep
post_max_sizeconservative andupload_max_filesizebelow it. Bound decoded request sizes, input nesting, multipart parts, and headers. - Use container or cgroup memory limits as an availability boundary. Do not substitute
RLIMIT_ASorRLIMIT_DATA, which can trigger the vulnerable allocation-failure path.
Removing PHP’s memory limit requires appropriate resource controls. These measures do not make an unpatched installation safe.
Reduce Stale-State Attack Paths
For CVE-2026-109619:
- Set
session.upload_progress.enabled=0before request parsing and restart every worker. Do not rely on application-levelini_set()or FPM.user.ini. - On PHP 8.5, set
fatal_error_backtraces=0and restart every worker. - Remove invalid or deprecated per-request settings that generate diagnostics before initialization. Hiding diagnostics does not prevent the vulnerable access.
- Address attacker-reachable fatal errors and execution timeouts.
These changes address specific paths rather than every stale-state variant.
Retain the upload-progress setting in accordance with PHP’s October 23 advisory described above.
Restrict Unnecessary Uploads and Review WAF Coverage
If an application does not require multipart requests, consider blocking multipart/form-data before requests reach PHP. Confirm the effect on legitimate functionality.
Where uploads are required, request-size limits and targeted WAF rules can reduce exposure, but do not cover every memory-handling or server-configuration path. Review body-inspection limits and handling of oversized requests when configuring protections.
AWS, Cloudflare, and Microsoft have published PHP2Shell guidance. Confirm which protections apply to your deployment and whether enabling rules could affect legitimate traffic. WAF protection supplements patching.
Monitor and Investigate
Review web server, PHP, proxy, and endpoint telemetry for:
- PHP worker processes launching shells or downloading tools.
- Unexpected process execution, files, or outbound connections.
- Suspicious multipart requests containing
PHP_SESSION_UPLOAD_PROGRESS. - Attempts to access environment variables or application configuration files.
The upload-progress field has legitimate uses; its presence alone does not establish compromise. AWS recommends investigating from at least October 17, based on its earliest observed attempt.
Preserve relevant logs and investigate suspected compromise separately. Patching and a negative check do not remove an existing compromise.
Embedded PHP and Vendor Products
Do not assume that updating the operating system’s PHP package fixes every bundled runtime. Review the relevant product advisory and use the vendor-supported update process.
Cisco’s advisory distinguishes confirmed vulnerable products, products under investigation, and products confirmed unaffected. Its findings illustrate why a PHP dependency alone does not establish identical exposure across products. Consult current vendor guidance for applicability and fixed releases.
Timeline
- October 17, 2026: Earliest PHP2Shell exploitation attempt subsequently reported by Amazon Threat Intelligence.
- October 20, 2026: PHP announced an upcoming critical security release.
- October 21, 2026: PHP released technical advisories and PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12.
- October 21, 2026: CISA urged immediate patching. Amazon Threat Intelligence reported pre-disclosure exploitation attempts.
- October 22, 2026: Additional telemetry documented scanning and exploitation attempts, with observations distinguishing attempts from confirmed compromise.
- October 23, 2026: PHP published additional session-upload-progress guidance for CVE-2026-115560.
- October 23, 2026: Horizon3 made a NodeZero Rapid Response check for PHP2Shell available to help identify indications of vulnerability. The check does not attempt full remote code execution, and a negative result does not rule out risk.
References
- PHP security updates and October 23 informational advisory
- CVE-2026-109618 technical advisory
- CVE-2026-109619 technical advisory
- CISA response guidance
- Amazon Threat Intelligence findings
- Cisco Talos observations
- Wordfence attack telemetry and assessment
- AWS WAF guidance
- Cloudflare WAF guidance
- Microsoft Azure WAF guidance
- Cisco product advisory
- Red Hat: CVE-2026-109618
- Red Hat: CVE-2026-109619