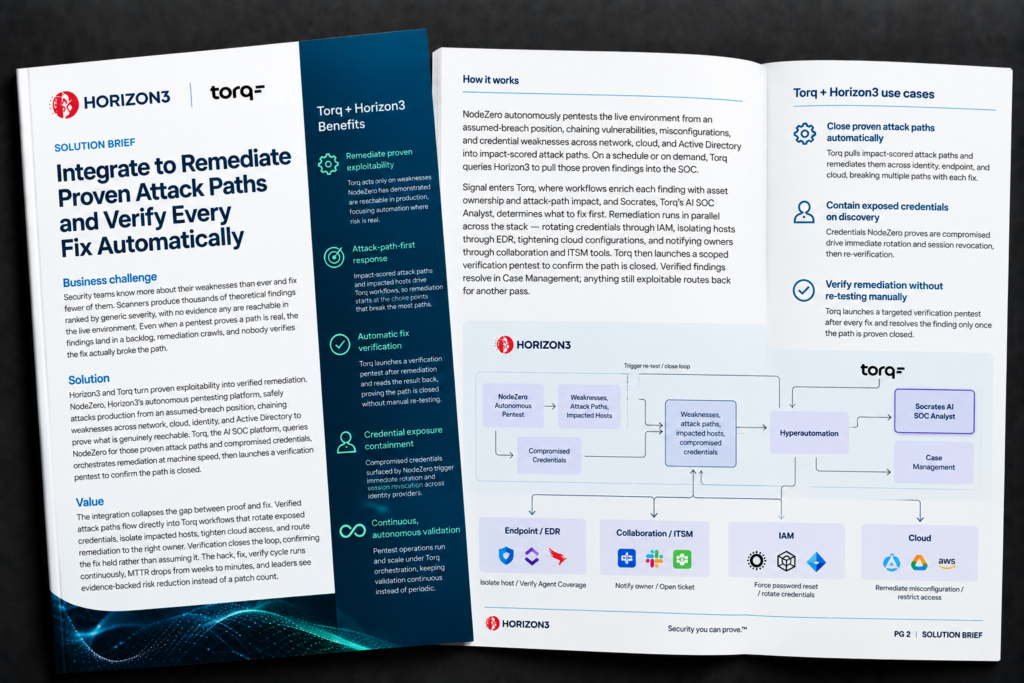
Security teams need more than a list of weaknesses. They need evidence of which attack paths are exploitable, a way to act on that evidence, and confirmation that remediation closed the path.
The Horizon3 and Torq joint solution brief explains how NodeZero® autonomous pentesting and Torq’s AI SOC platform connect proven exploitability with automated remediation and verification.
Connect Proof to Remediation
NodeZero safely tests the live environment from an assumed-breach position, chaining vulnerabilities, misconfigurations, and credential weaknesses across network, cloud, identity, and Active Directory to demonstrate reachable attack paths.
Torq brings those findings into SOC workflows, enriching them with asset ownership and attack-path impact. Teams can use this context to focus remediation on the weaknesses NodeZero has demonstrated are exploitable.
Verify That the Fix Held
The integration connects remediation with a scoped verification pentest. Torq can orchestrate actions across identity, endpoint, cloud, collaboration, and ITSM tools, then launch a targeted retest to confirm that the attack path is closed.
Verified findings resolve in Case Management. Findings that remain exploitable return for another remediation pass, supporting a continuous hack, fix, verify cycle.
Explore the Integration’s Use Cases
The brief shows how Horizon3 and Torq work together to:
- Close proven attack paths: Use impact-scored findings to direct remediation across identity, endpoint, and cloud.
- Contain exposed credentials: Trigger credential rotation and session revocation, followed by verification.
- Verify remediation automatically: Retest after remediation and resolve a finding once the path is proven closed.
The document also illustrates how NodeZero findings flow into Torq Hyperautomation, Socrates AI SOC Analyst, and Case Management, connecting proven weaknesses with coordinated action and verified outcomes.
Download the Horizon3 + Torq Joint Solution Brief
See how Horizon3 and Torq connect proven attack paths, automated remediation, and verification in a continuous security workflow.