CVE-2026-123158
OpenSSH musl Password Authentication Bypass & Remote Code Execution Vulnerability (*sshole)
CVE-2026-123158, known as *sshole, is an authentication bypass in OpenSSH sshd before 10.6p2 on Linux systems that use musl libc without PAM. It affects products that run OpenSSH on musl, such as Alpine Linux (in its default configuration), OpenWrt, and other embedded devices. A remote attacker who knows the name of an account with no password set (a * in its password field) can log in as that account and run commands by sending an overly long password, which musl turns into the same *. Password authentication must be enabled. MITRE rates the flaw CVSS 3.1 8.1 (High). Public proofs of concept exist, and exploitation in the wild has been confirmed.
Technical Details
The flaw is in how sshd checks passwords on systems built with the musl C library and without PAM. Accounts with no password set, such as key-only users, store a * in their password field. When an attacker sends a very long password, musl also produces *, so the two match and the attacker logs in without credentials and can run commands as that account. If that account has administrative rights, the attacker gets root.
Stop Guessing, Start Proving
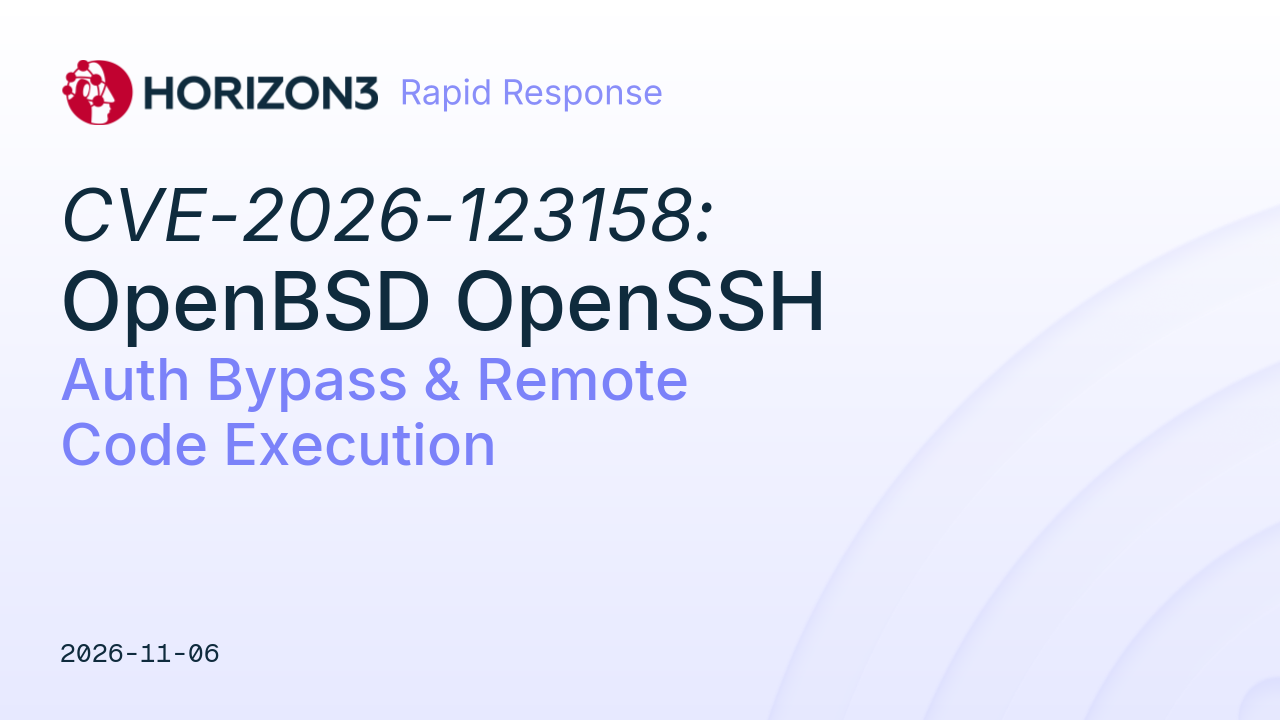
NodeZero® Proactive Security Platform: Rapid Response
A NodeZero Rapid Response test is available to safely validate whether this vulnerability can be exploited in your environment.
- Run the Rapid Response test: Launch the test from NodeZero to validate exploitability.
- Patch immediately: Upgrade to a fixed version or apply vendor-recommended mitigations.
- Re-run the test: Verify that the vulnerability is no longer exploitable after remediation.
Affected Versions & Patch
Affected
- OpenSSH sshd before 10.6p2 on Linux, built with musl libc and without PAM
- Products that run OpenSSH on musl, such as Alpine Linux (3.16 through 3.24 and edge), OpenWrt, and embedded devices
Fixed
- OpenSSH 10.6p2
- Alpine Linux backports: edge 10.6_p2-r0, 3.24 10.3_p1-r2, 3.23 10.2_p1-r1, 3.22 10.0_p1-r11, 3.21 9.9_p2-r1. Fixes for 3.16 through 3.20 are listed in the Alpine advisory.
Mitigations
- If you cannot upgrade yet, set PasswordAuthentication no and restart sshd. This blocks the attack but is not a fix; upgrade when possible.
Timeline
- November 5, 2026: OpenSSH releases 10.6p2 with the fix.
- November 5, 2026: Alpine Linux publishes a security advisory and patched packages.
- November 5, 2026: CVE-2026-123158 is published.
- November 6, 2026: Horizon3 releases a NodeZero Rapid Response test.