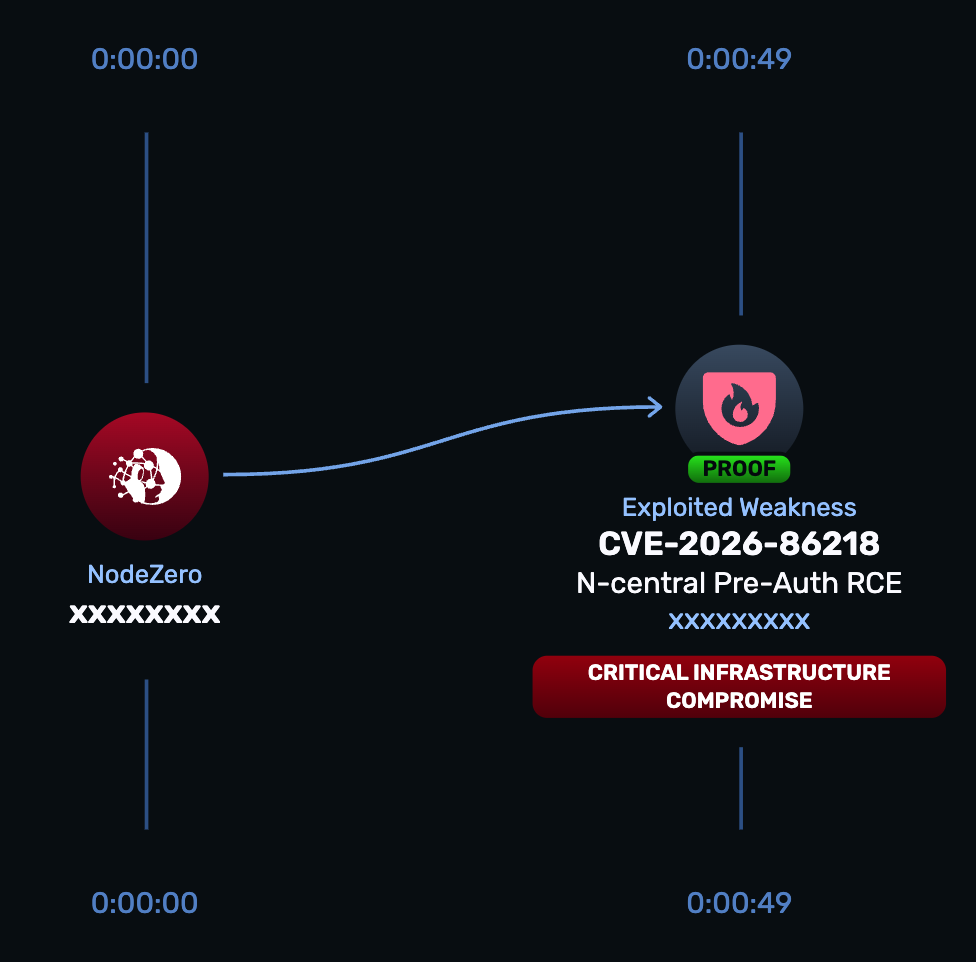
CVE-2026-86218
N-able N-central Pre-Authentication Remote Code Execution Vulnerability
CVE-2026-86218 is a critical pre-authentication remote code execution vulnerability affecting N-able N-central. An unauthenticated attacker with network access to a vulnerable N-central server could exploit the vulnerability to execute code without user interaction. N-able assigned it a CVSS 4.0 score of 10.0, while NIST assigned it a CVSS 3.1 score of 9.8. CISA added CVE-2026-86218 to its Known Exploited Vulnerabilities catalog based on evidence of active exploitation.
Technical Details
CVE-2026-86218 affects the N-central server and is remotely exploitable without authentication or user interaction. The official CVE record classifies the vulnerability as CWE-96, Improper Neutralization of Directives in Statically Saved Code, also known as static code injection.
Successful exploitation could allow an attacker to execute code on the N-central server, affecting the confidentiality, integrity, and availability of the system. The vulnerability has low attack complexity and requires no privileges.
CISA has confirmed that CVE-2026-86218 is being exploited. However, public reporting about specific N-central intrusions also involves other recently disclosed vulnerabilities, and researchers have not conclusively attributed every observed compromise to CVE-2026-86218.
Stop Guessing, Start Proving
NodeZero® Proactive Security Platform — Rapid Response
A NodeZero Rapid Response test has been developed to safely validate whether CVE-2026-86218 can be exploited in your environment. The test executes real attack techniques without causing damage, giving teams immediate clarity on exposure.
- Run the Rapid Response test: Launch from the NodeZero platform to determine whether remote code execution is possible
- Patch immediately: Upgrade self-hosted N-central deployments to version 2026.3.1.14
- Re-run the test: Confirm the vulnerability is no longer exploitable after remediation
Affected Versions & Patch
Affected
N-able N-central versions before 2026.3.1.14 are affected.
Fixed
N-able addressed CVE-2026-86218 in N-central 2026.3 Hotfix 4, build 2026.3.1.14. Customers operating on-premises N-central deployments should upgrade immediately.
N-able has already applied the patch to hosted N-central environments, also referred to as NCOD. Customers using hosted instances do not need to take action.
Mitigations
N-able directs customers with on-premises deployments to upgrade to version 2026.3.1.14. The vendor has not identified an alternative remediation in its public release notes.
If an upgrade cannot be completed immediately, restrict access to the N-central console from the public internet and other untrusted networks. This is a risk-reduction measure and does not remediate the vulnerability.
Because exploitation has been reported, organizations should also review N-central accounts, appliance logs, and administrative activity for signs of unauthorized access. Applying the hotfix does not determine whether a system was compromised before it was patched.
Timeline
- September 5, 2026: N-able released N-central 2026.3 Hotfix 4, build 2026.3.1.14, addressing CVE-2026-86218.
- September 6, 2026: CVE-2026-86218 was published.
- September 8, 2026: CISA added CVE-2026-86218 to its Known Exploited Vulnerabilities catalog based on evidence of active exploitation.
- September 15, 2026: Horizon3 released a NodeZero Rapid Response test for CVE-2026-86218.
References
- N-able Security Advisory
- N-able N-central 2026.3 Hotfix 4 Release Notes
- CVE.org Record – CVE-2026-86218
- NIST NVD – CVE-2026-86218
- CISA Adds Four Known Exploited Vulnerabilities to Catalog
- The Hacker News: N-able N-central Pre-Auth RCE Flaw Exploited in the Wild
- Help Net Security: N-able Patches Critical N-central Zero-Day Exploited in the Wild