Enterprise Leadership
SEARCH
CATEGORIES
TAGS
From Evidence to Action: Scaling CTEM Across the Enterprise
In this webinar, Ellen Sundra, VP, Customers at Horizon3; and Dan DeCloss, Chief Customer Officer at Brinqa, will explore how unified exposure data, attacker-derived evidence, business context, and remediation orchestration can transform proof into prioritized, coordinated action.

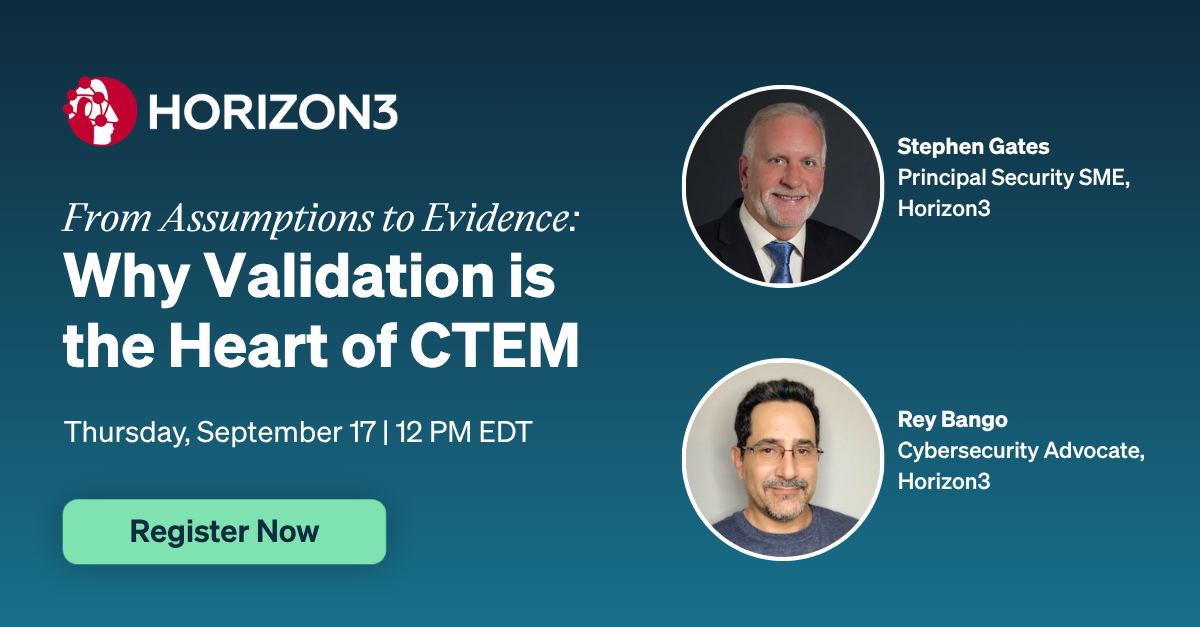
From Assumptions to Evidence: Why Validation Is the Heart of CTEM
In this webinar, we'll explore why validation has become one of the most important phases of CTEM, how organizations can move from assumptions to evidence, and why proof is often the difference between debating a finding and taking action.
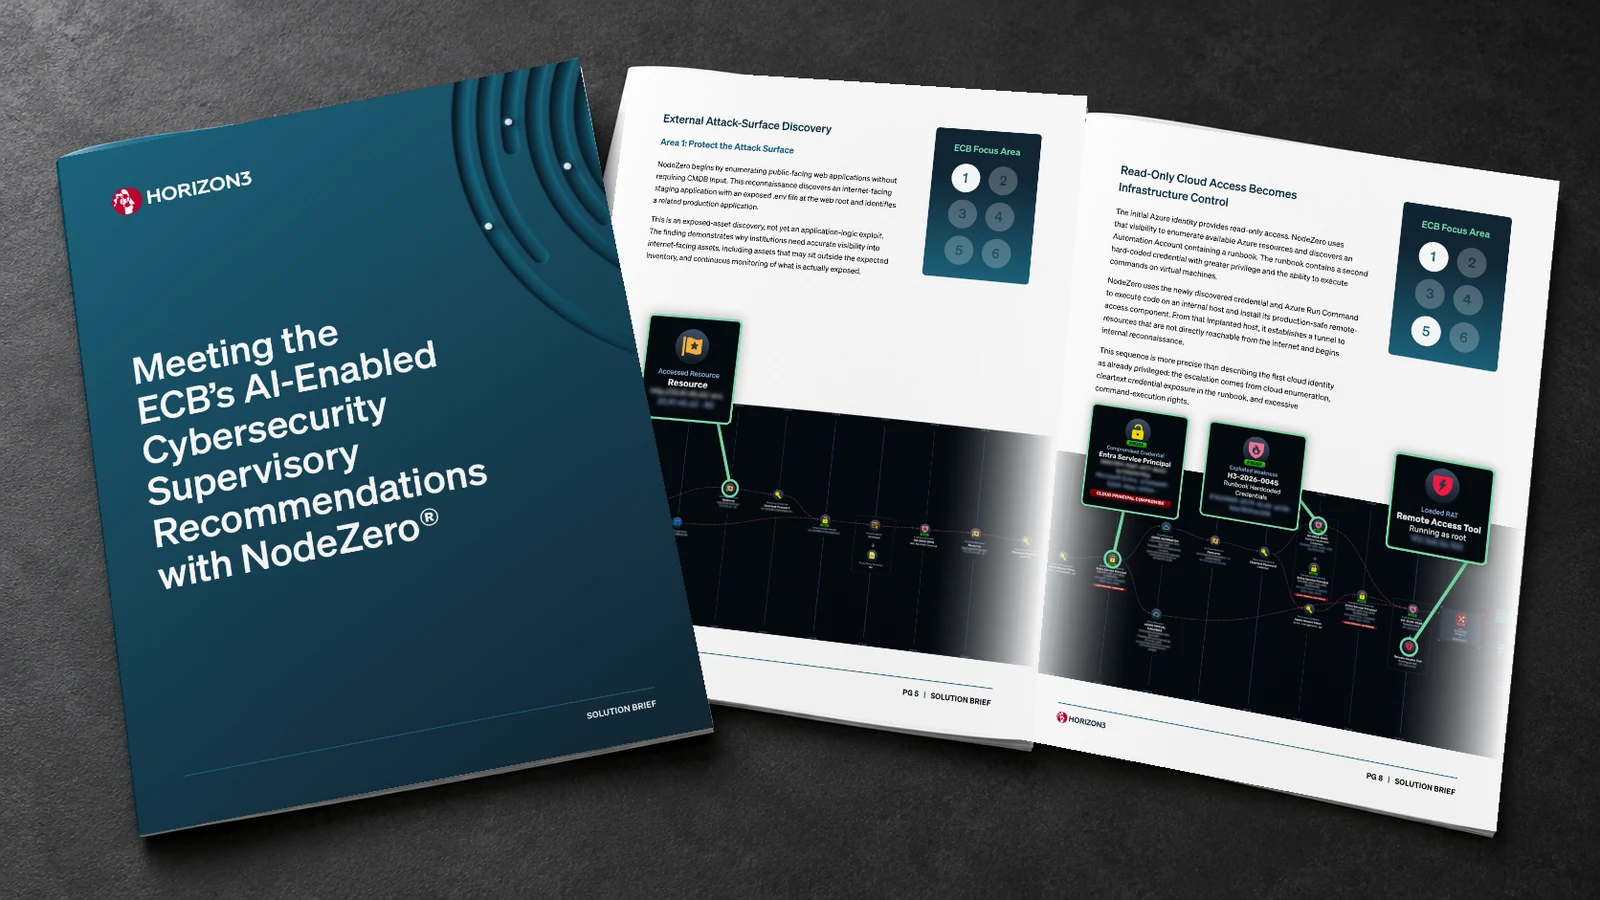
Meeting the ECB’s AI-Enabled Cybersecurity Supervisory Recommendations with NodeZero®
October 16, 2026
Explore how NodeZero autonomous penetration testing connects application, cloud, identity, and infrastructure weaknesses into validated attack paths, helping banks prioritize remediation and build evidence for the ECB’s cybersecurity supervisory recommendations.
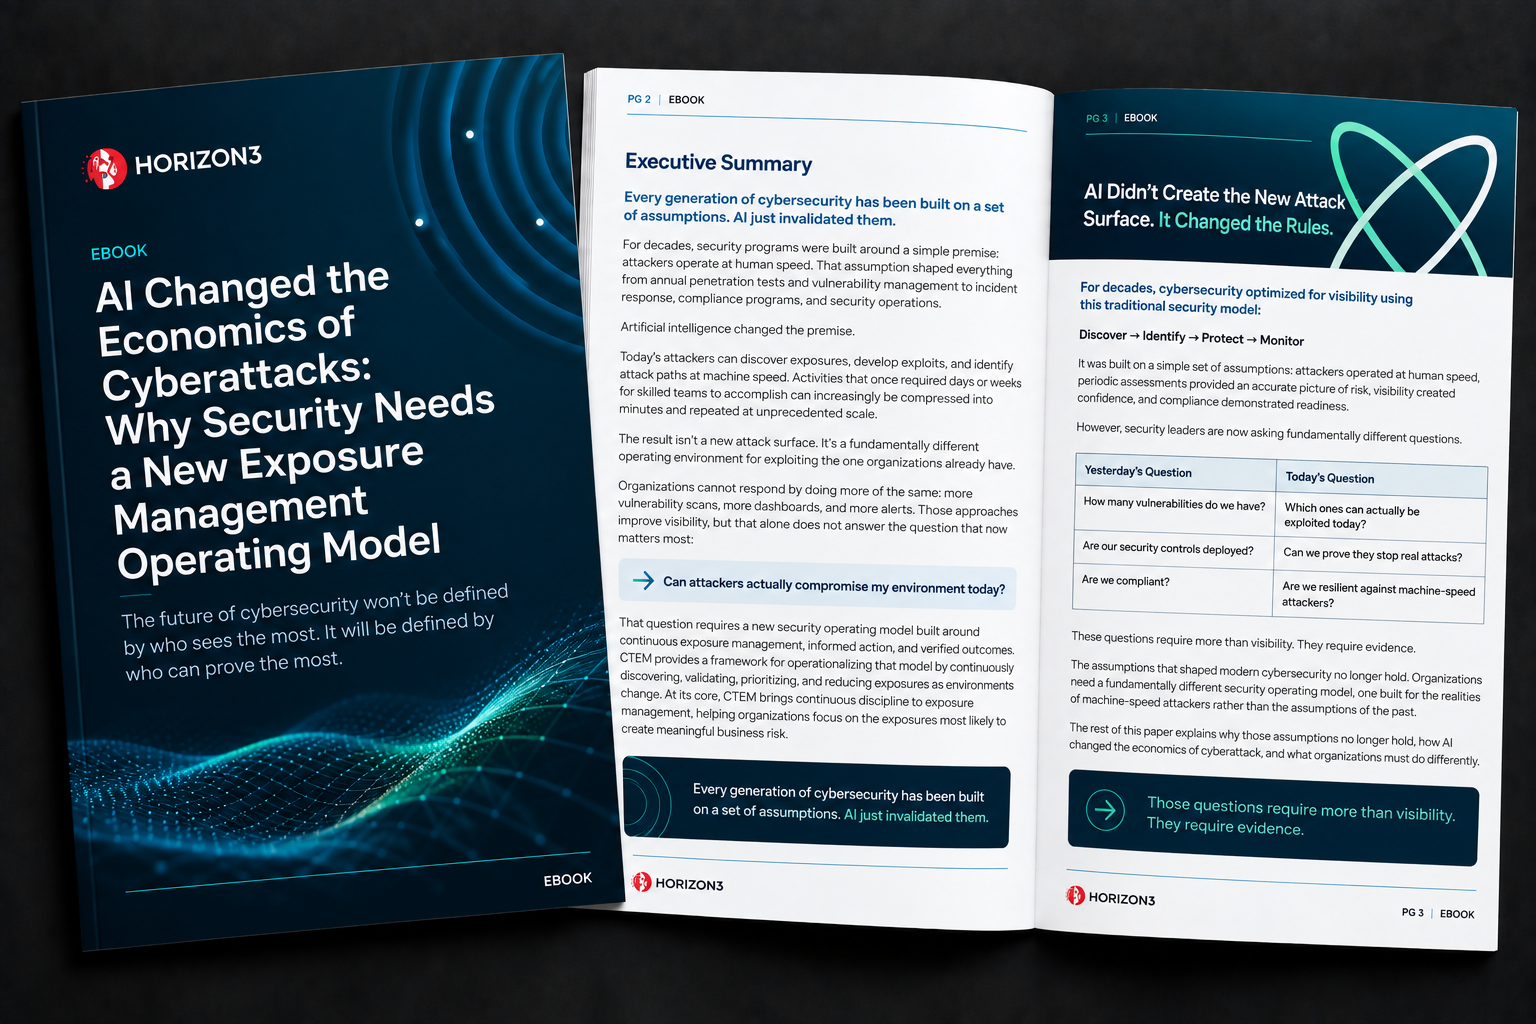
AI Changed the Economics of Cyberattacks
October 9, 2026
AI has changed the speed, scale, and economics of cyberattacks. Learn why modern security requires continuous exposure management built around evidence, informed action, and verified outcomes.
HacktoberFest: A Fireside Chat with Horizon3 & GuidePoint Security
Continuous Validation, Real-World Risk, and Proving Security Impact Join top subject matter experts from Horizon3 and GuidePoint Security for a candid conversation on the evolving cybersecurity landscape and what organizations can do to strengthen their defenses.

What Security Metrics Actually Matter?
October 1, 2026
Security activity doesn’t always equal risk reduction. Learn how attack paths, business impact, verification, remediation speed, and recurrence can show whether CTEM is actually working.
CTEM Buyer’s Guide: How to Evaluate the Technologies That Turn Continuous Threat Exposure Management Into an Operating Model
September 17, 2026
Learn how to evaluate CTEM technologies based on what they can prove, from exploitable attack paths and remediation priorities to verification and measurable risk reduction.
CyberCom 2.0 and the Revolution in AI-Enabled Offensive Cyber Operations
September 17, 2026
AI is transforming the speed, scale, and economics of offensive cyber operations. Explore how CyberCom 2.0 can help lay the foundation for the next era of AI-enabled American cyber power.
CTEM Technology Evaluation Scorecard
September 16, 2026
Use the CTEM Technology Evaluation Scorecard to assess technologies across the CTEM operating model, score capabilities based on demonstrated evidence, and identify critical validation and verification gaps.

CISO’s CTEM Evaluation Checklist
September 16, 2026
Use the CISO’s CTEM Evaluation Checklist to assess whether technologies supporting your CTEM program can prove exploitability, demonstrate attack impact, verify remediation, and show measurable exposure reduction.
