Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-9082 is a highly critical SQL injection vulnerability in Drupal core affecting PostgreSQL-backed deployments. The flaw allows unauthenticated attackers to execute arbitrary SQL queries and potentially compromise affected environments.
Read More →CVE-2026-23734 is a critical path traversal vulnerability affecting XWiki’s xwiki-commons-classloader-api component. The flaw may allow unauthenticated attackers to access sensitive configuration files through crafted ssx and jsx endpoint requests.
Read More →Featured
WEBINAR REPLAY
SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
CVE-2025-64446
November 14, 2025
Fortinet FortiWeb Authentication Bypass via Path Traversal Vulnerability

CVE-2025-9316, CVE-2025-11700
November 13, 2025
N-able N-central Vulnerabilities

CVE-2025-12480
November 13, 2025
Gladinet Triofox Improper Access Control Vulnerability | Active Exploitation

Hack The Box – Retro
November 10, 2025
NodeZero® autonomously solved Hack The Box Retro in just 11 minutes, chaining SMB guest access and weak credentials into an ADCS privilege escalation. This demonstration highlights how autonomous pentesting uncovers exploit chains and validates real attack paths, proving Horizon3’s commitment to evidence-based, attacker-validated security.

Introducing NodeZero® Advanced Data Pilfering: View Your Data Through the Eyes of an Attacker
NodeZero’s Advanced Data Pilfering uses LLMs to find hidden credentials and classify compromised files—revealing attacker paths and the real business risk in unstructured data.

CVE-2025-59287
October 31, 2025
WatchGuard Firebox / Fireware OS iked Out‑of‑Bounds Write RCE
CVE‑2025‑9242
October 29, 2025
WatchGuard Firebox / Fireware OS iked Out‑of‑Bounds Write
From Awareness to Assurance: Turning Cybersecurity Awareness Month into a Year-Round Practice
October 29, 2025
Cybersecurity awareness training builds knowledge—but not proof. This post shows how to evolve from education to validation by continuously testing your defenses with NodeZero®. Discover how real-world verification closes policy gaps, exposes hidden risks, and transforms one month of awareness into year-round assurance your security truly works.

Why Open-Source AI Pentesting Could Be Your Next Security Incident
October 23, 2025
Open-source AI pentesting frameworks can unintentionally transmit sensitive pentest data to external LLM APIs, creating hidden security, compliance, and governance risks for enterprises.

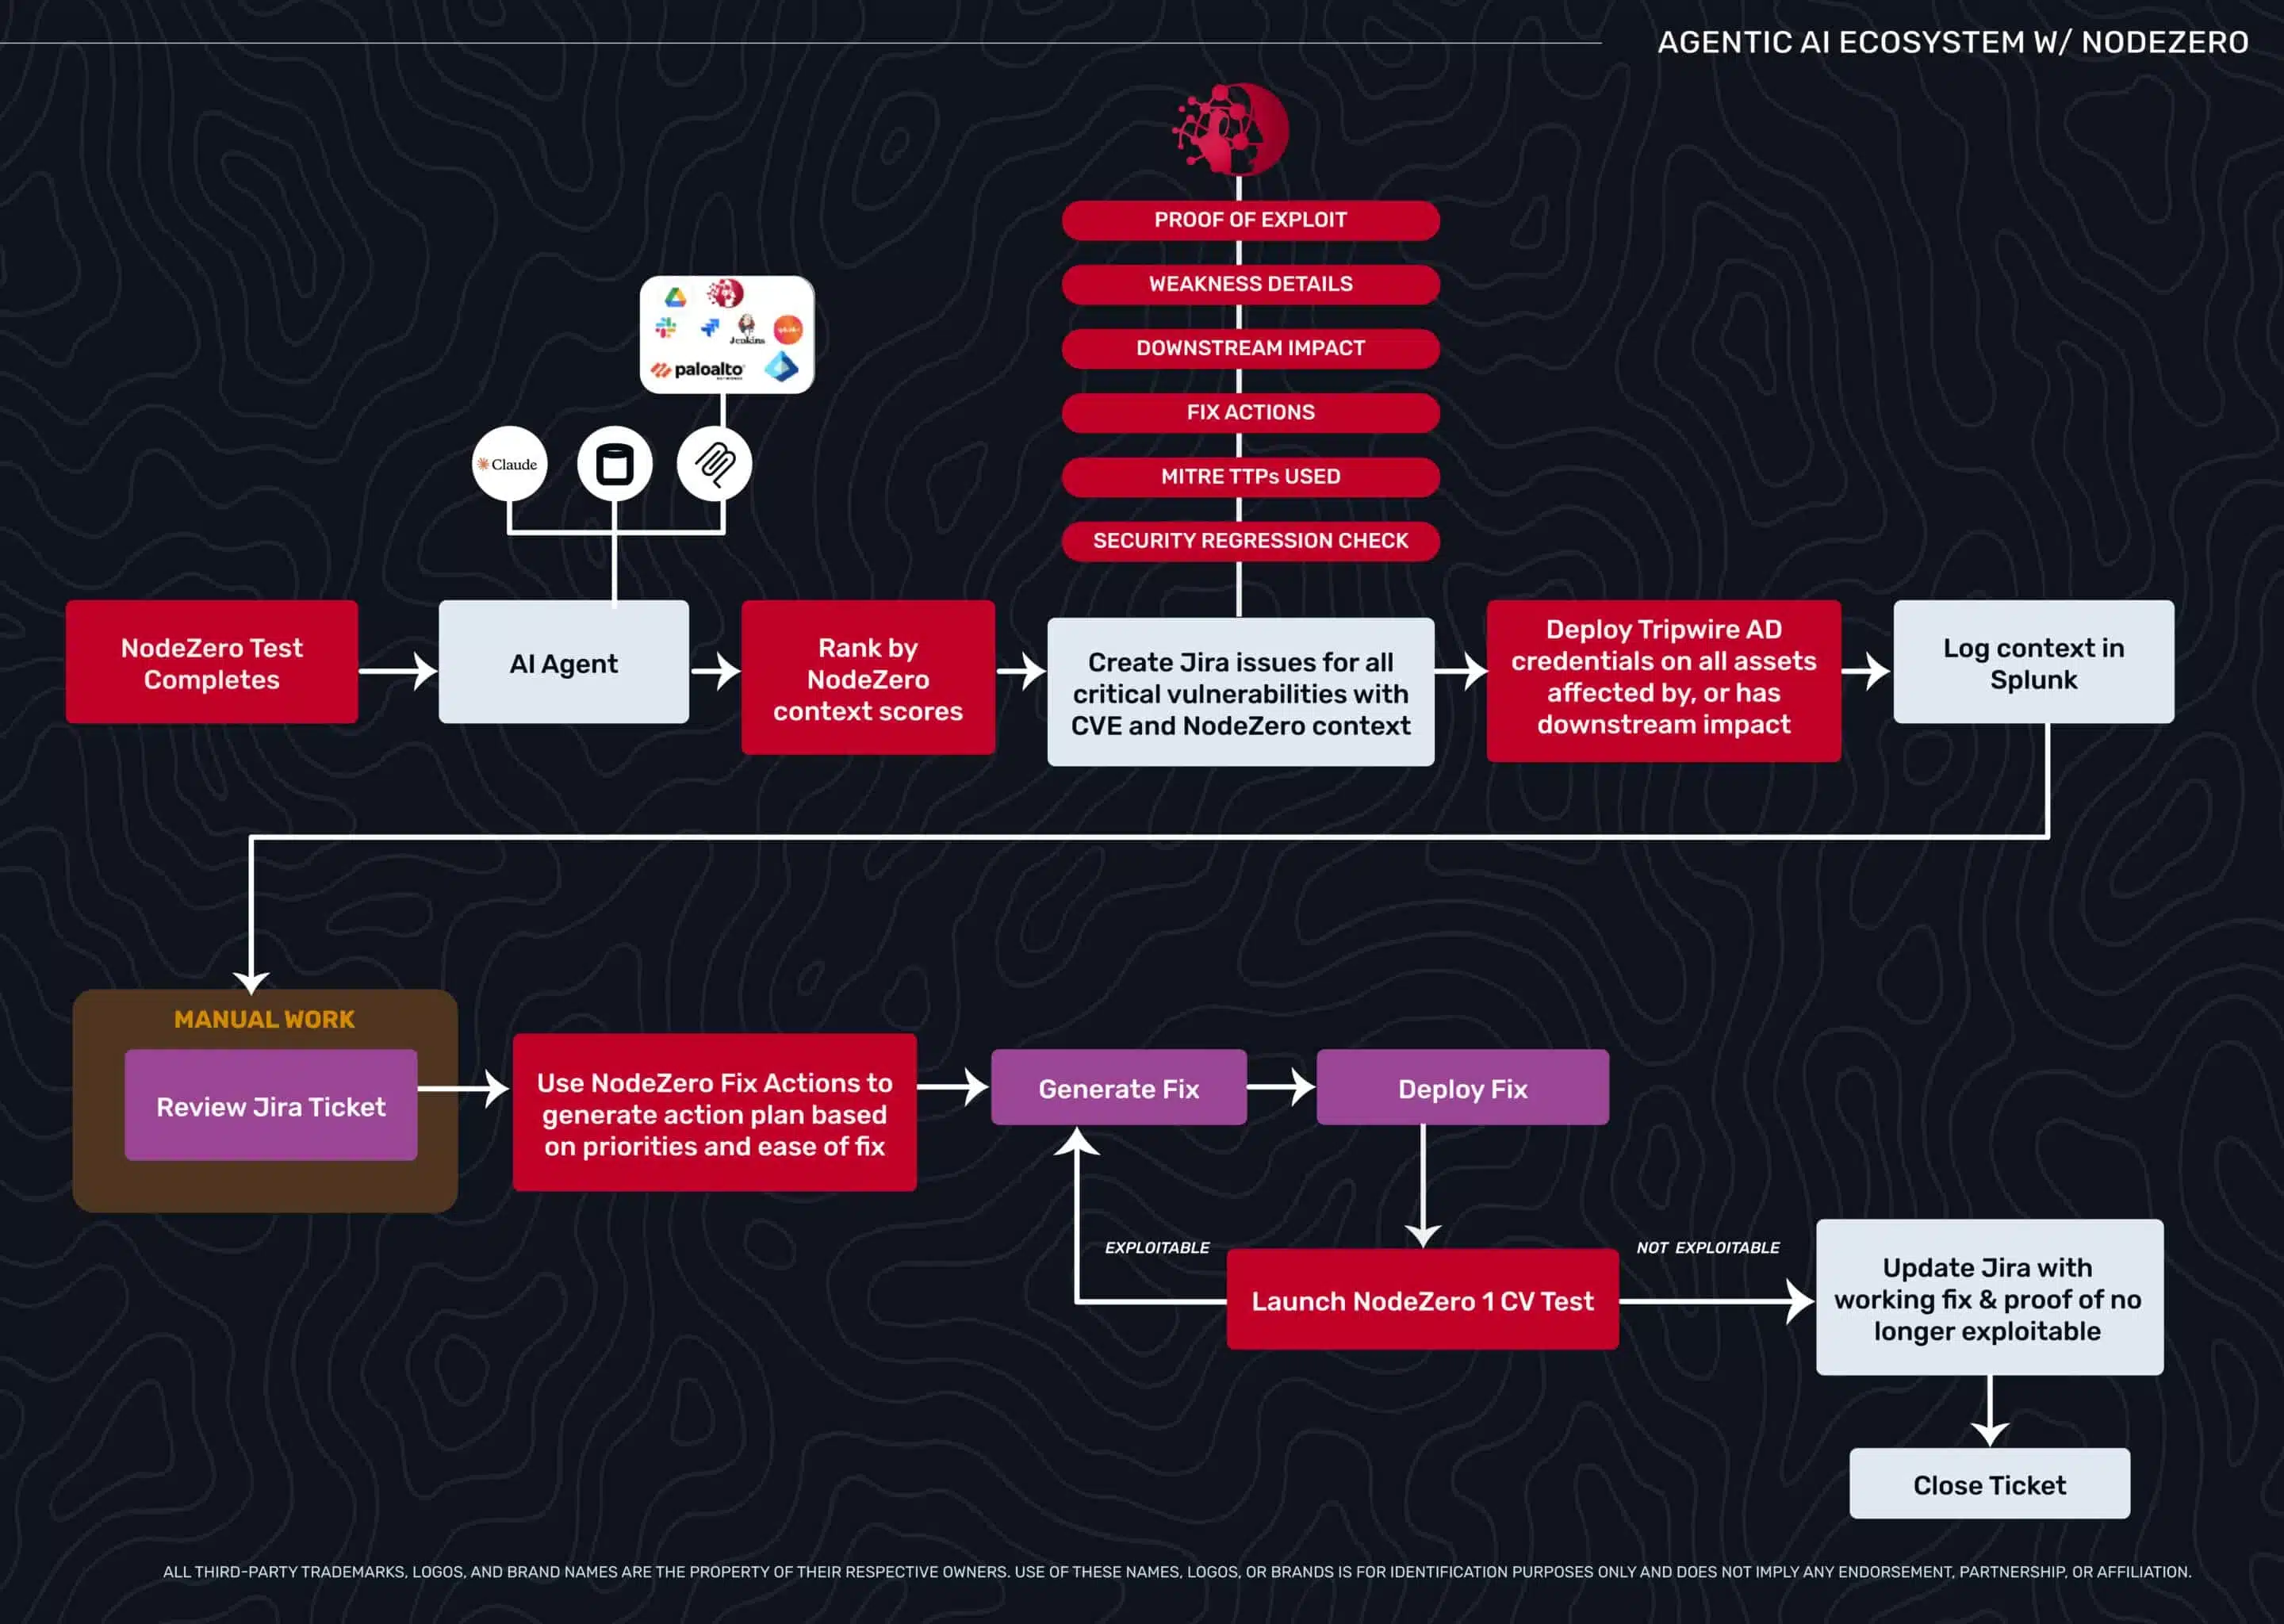
Building FixOps: Architectural Considerations for Autonomous Security Workflows
Designing reliable autonomous security workflows requires more than AI and automation—it demands solid architecture. This guide explores orchestration frameworks, integration points, scaling strategies, and human oversight models that help teams move from prototypes to production-ready FixOps systems built for resilience, precision, and continuous verification at scale.