Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-21643 allows unauthenticated SQL injection in FortiClient EMS, enabling code execution. Patch immediately and validate exposure.
Read More →CVE-2026-20160 enables unauthenticated command execution in Cisco SSM On-Prem. Patch immediately and validate exposure.
Read More →WEBINAR REPLAY
SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
CVE‑2025‑9242
October 29, 2025
WatchGuard Firebox / Fireware OS iked Out‑of‑Bounds Write
From Awareness to Assurance: Turning Cybersecurity Awareness Month into a Year-Round Practice
October 29, 2025
Cybersecurity awareness training builds knowledge—but not proof. This post shows how to evolve from education to validation by continuously testing your defenses with NodeZero®. Discover how real-world verification closes policy gaps, exposes hidden risks, and transforms one month of awareness into year-round assurance your security truly works.

Why Open-Source AI Pentesting Could Be Your Next Security Incident
October 23, 2025
Open-source AI pentesting frameworks can unintentionally transmit sensitive pentest data to external LLM APIs, creating hidden security, compliance, and governance risks for enterprises.

Building FixOps: Architectural Considerations for Autonomous Security Workflows
Designing reliable autonomous security workflows requires more than AI and automation—it demands solid architecture. This guide explores orchestration frameworks, integration points, scaling strategies, and human oversight models that help teams move from prototypes to production-ready FixOps systems built for resilience, precision, and continuous verification at scale.
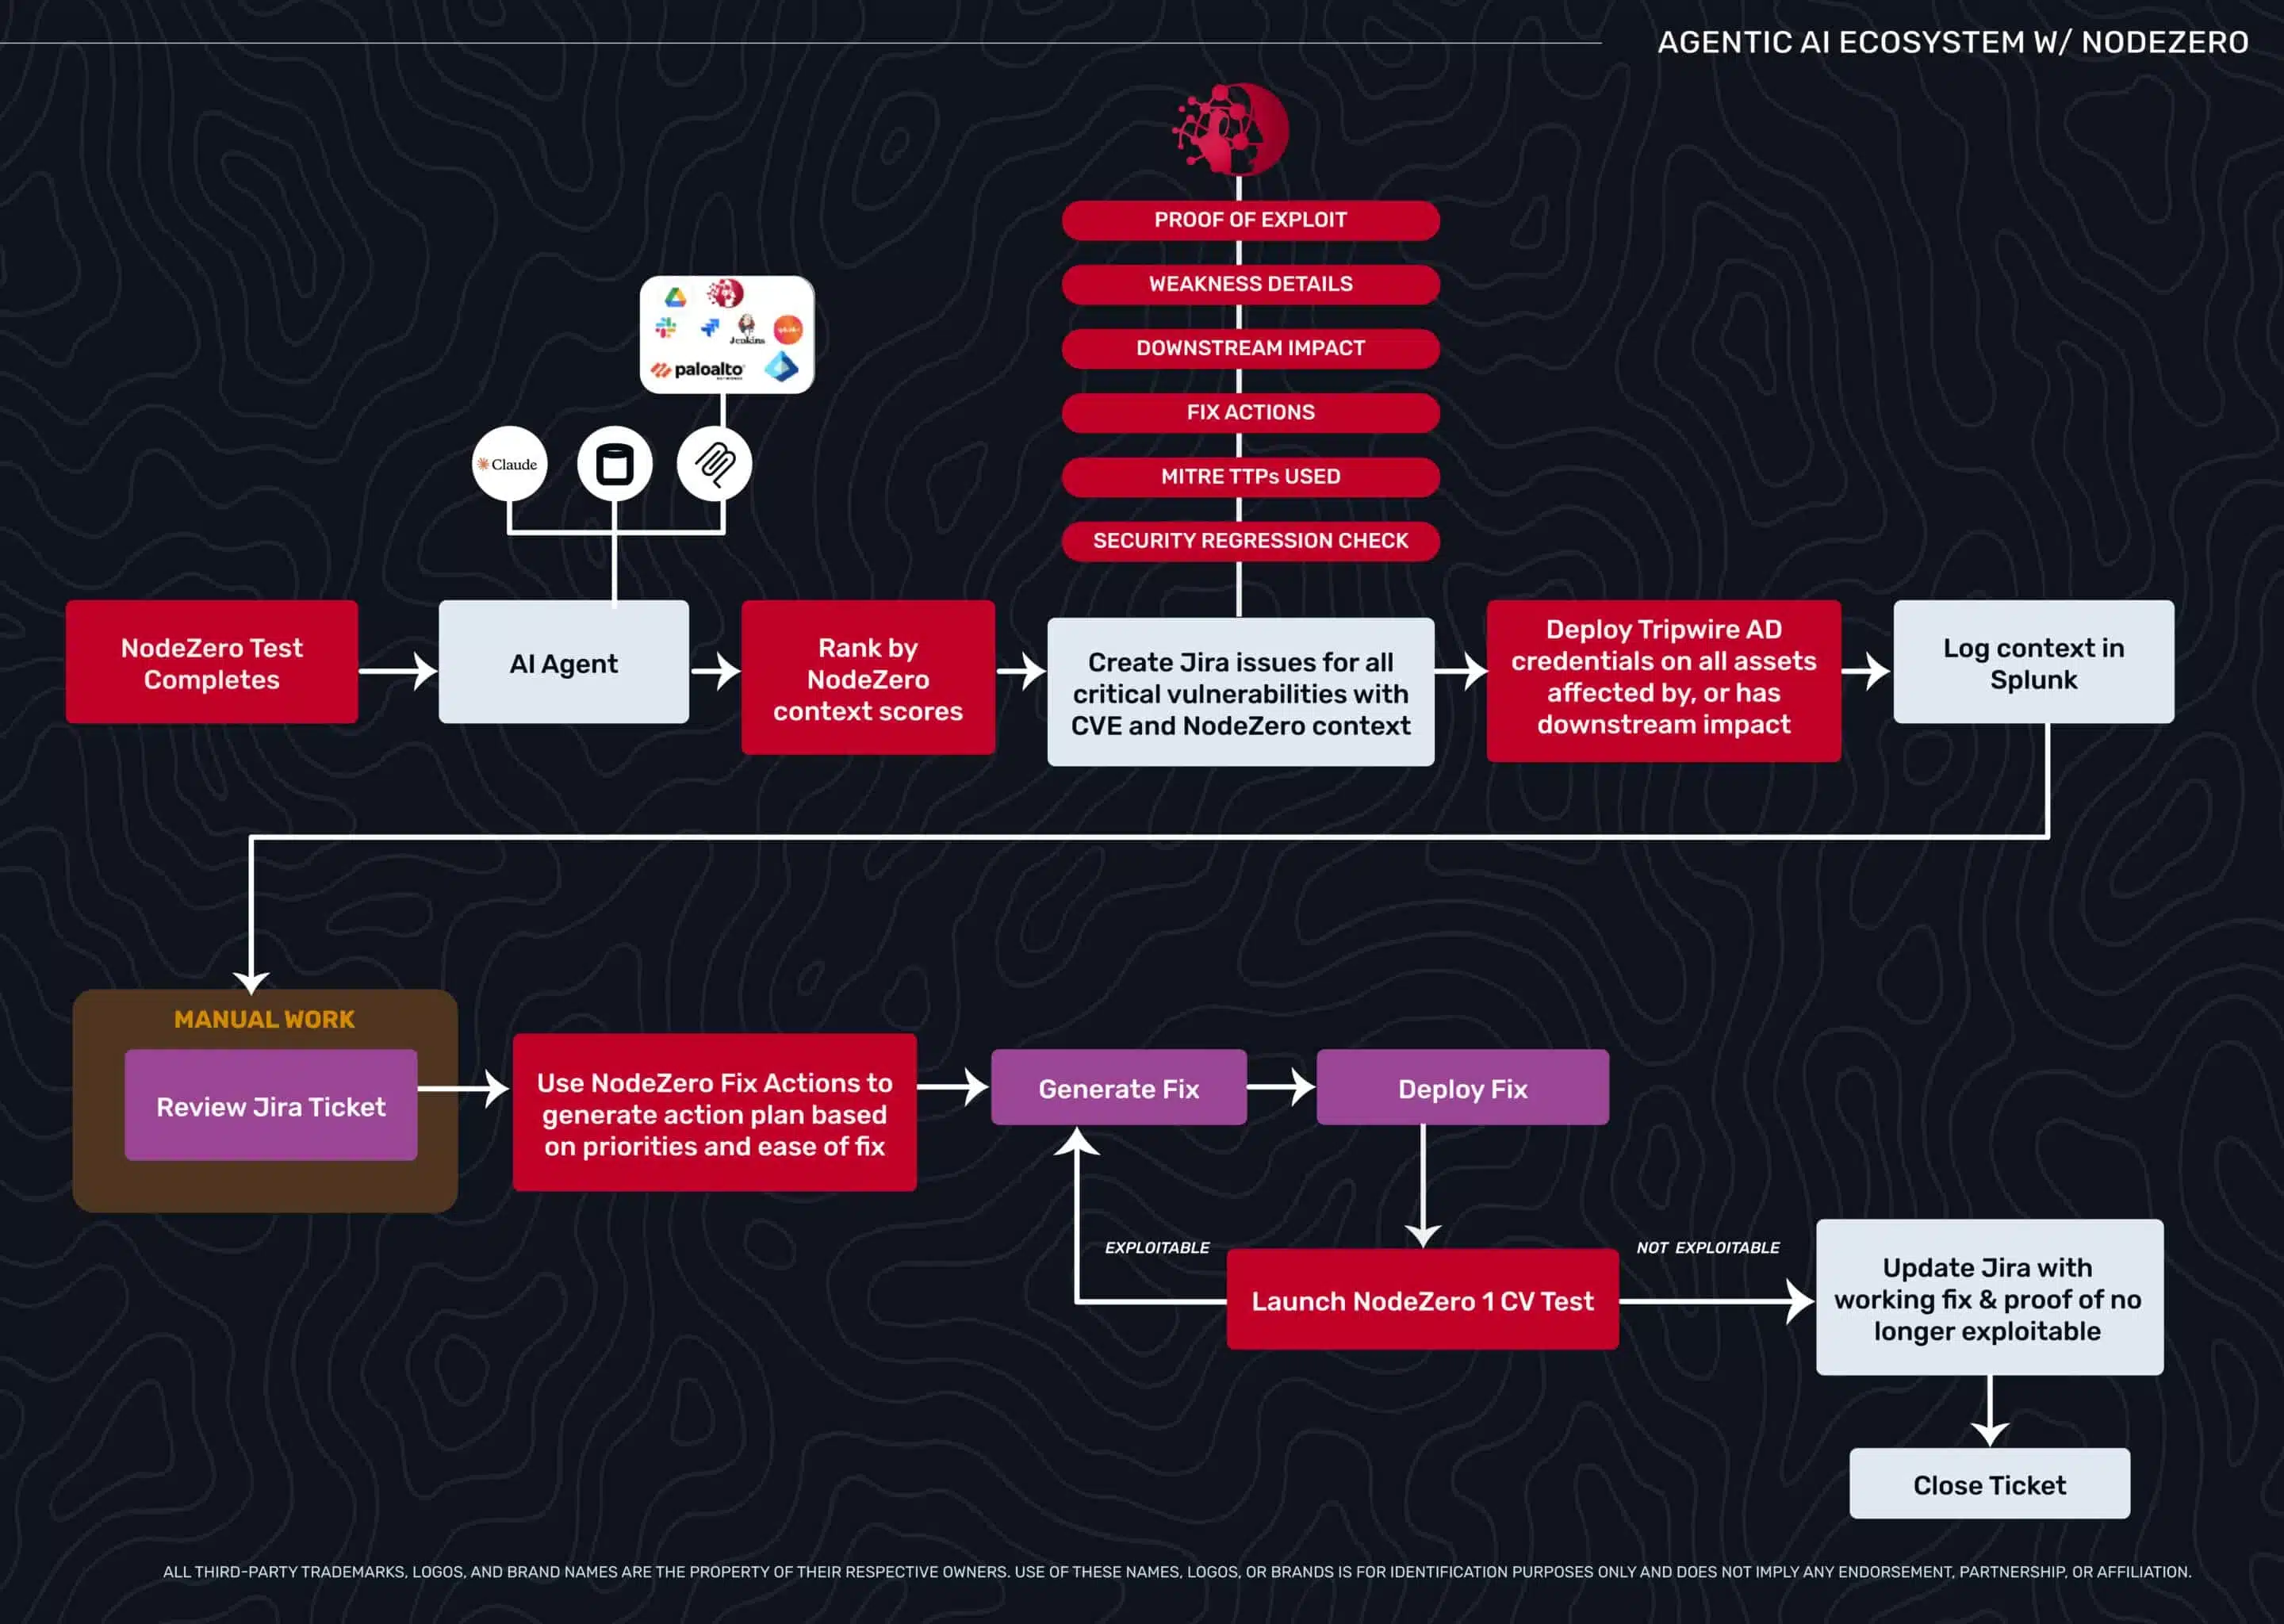
Beyond Triage: How Exploitability Data Transforms Agentic Security Workflows
Security teams drown in critical CVEs that don’t matter while missing medium flaws that lead to domain admin. This blog explores how exploitability data—validated through autonomous pentesting—enables agentic AI workflows to move beyond triage, prioritize what’s truly exploitable, and automate verification with confidence.
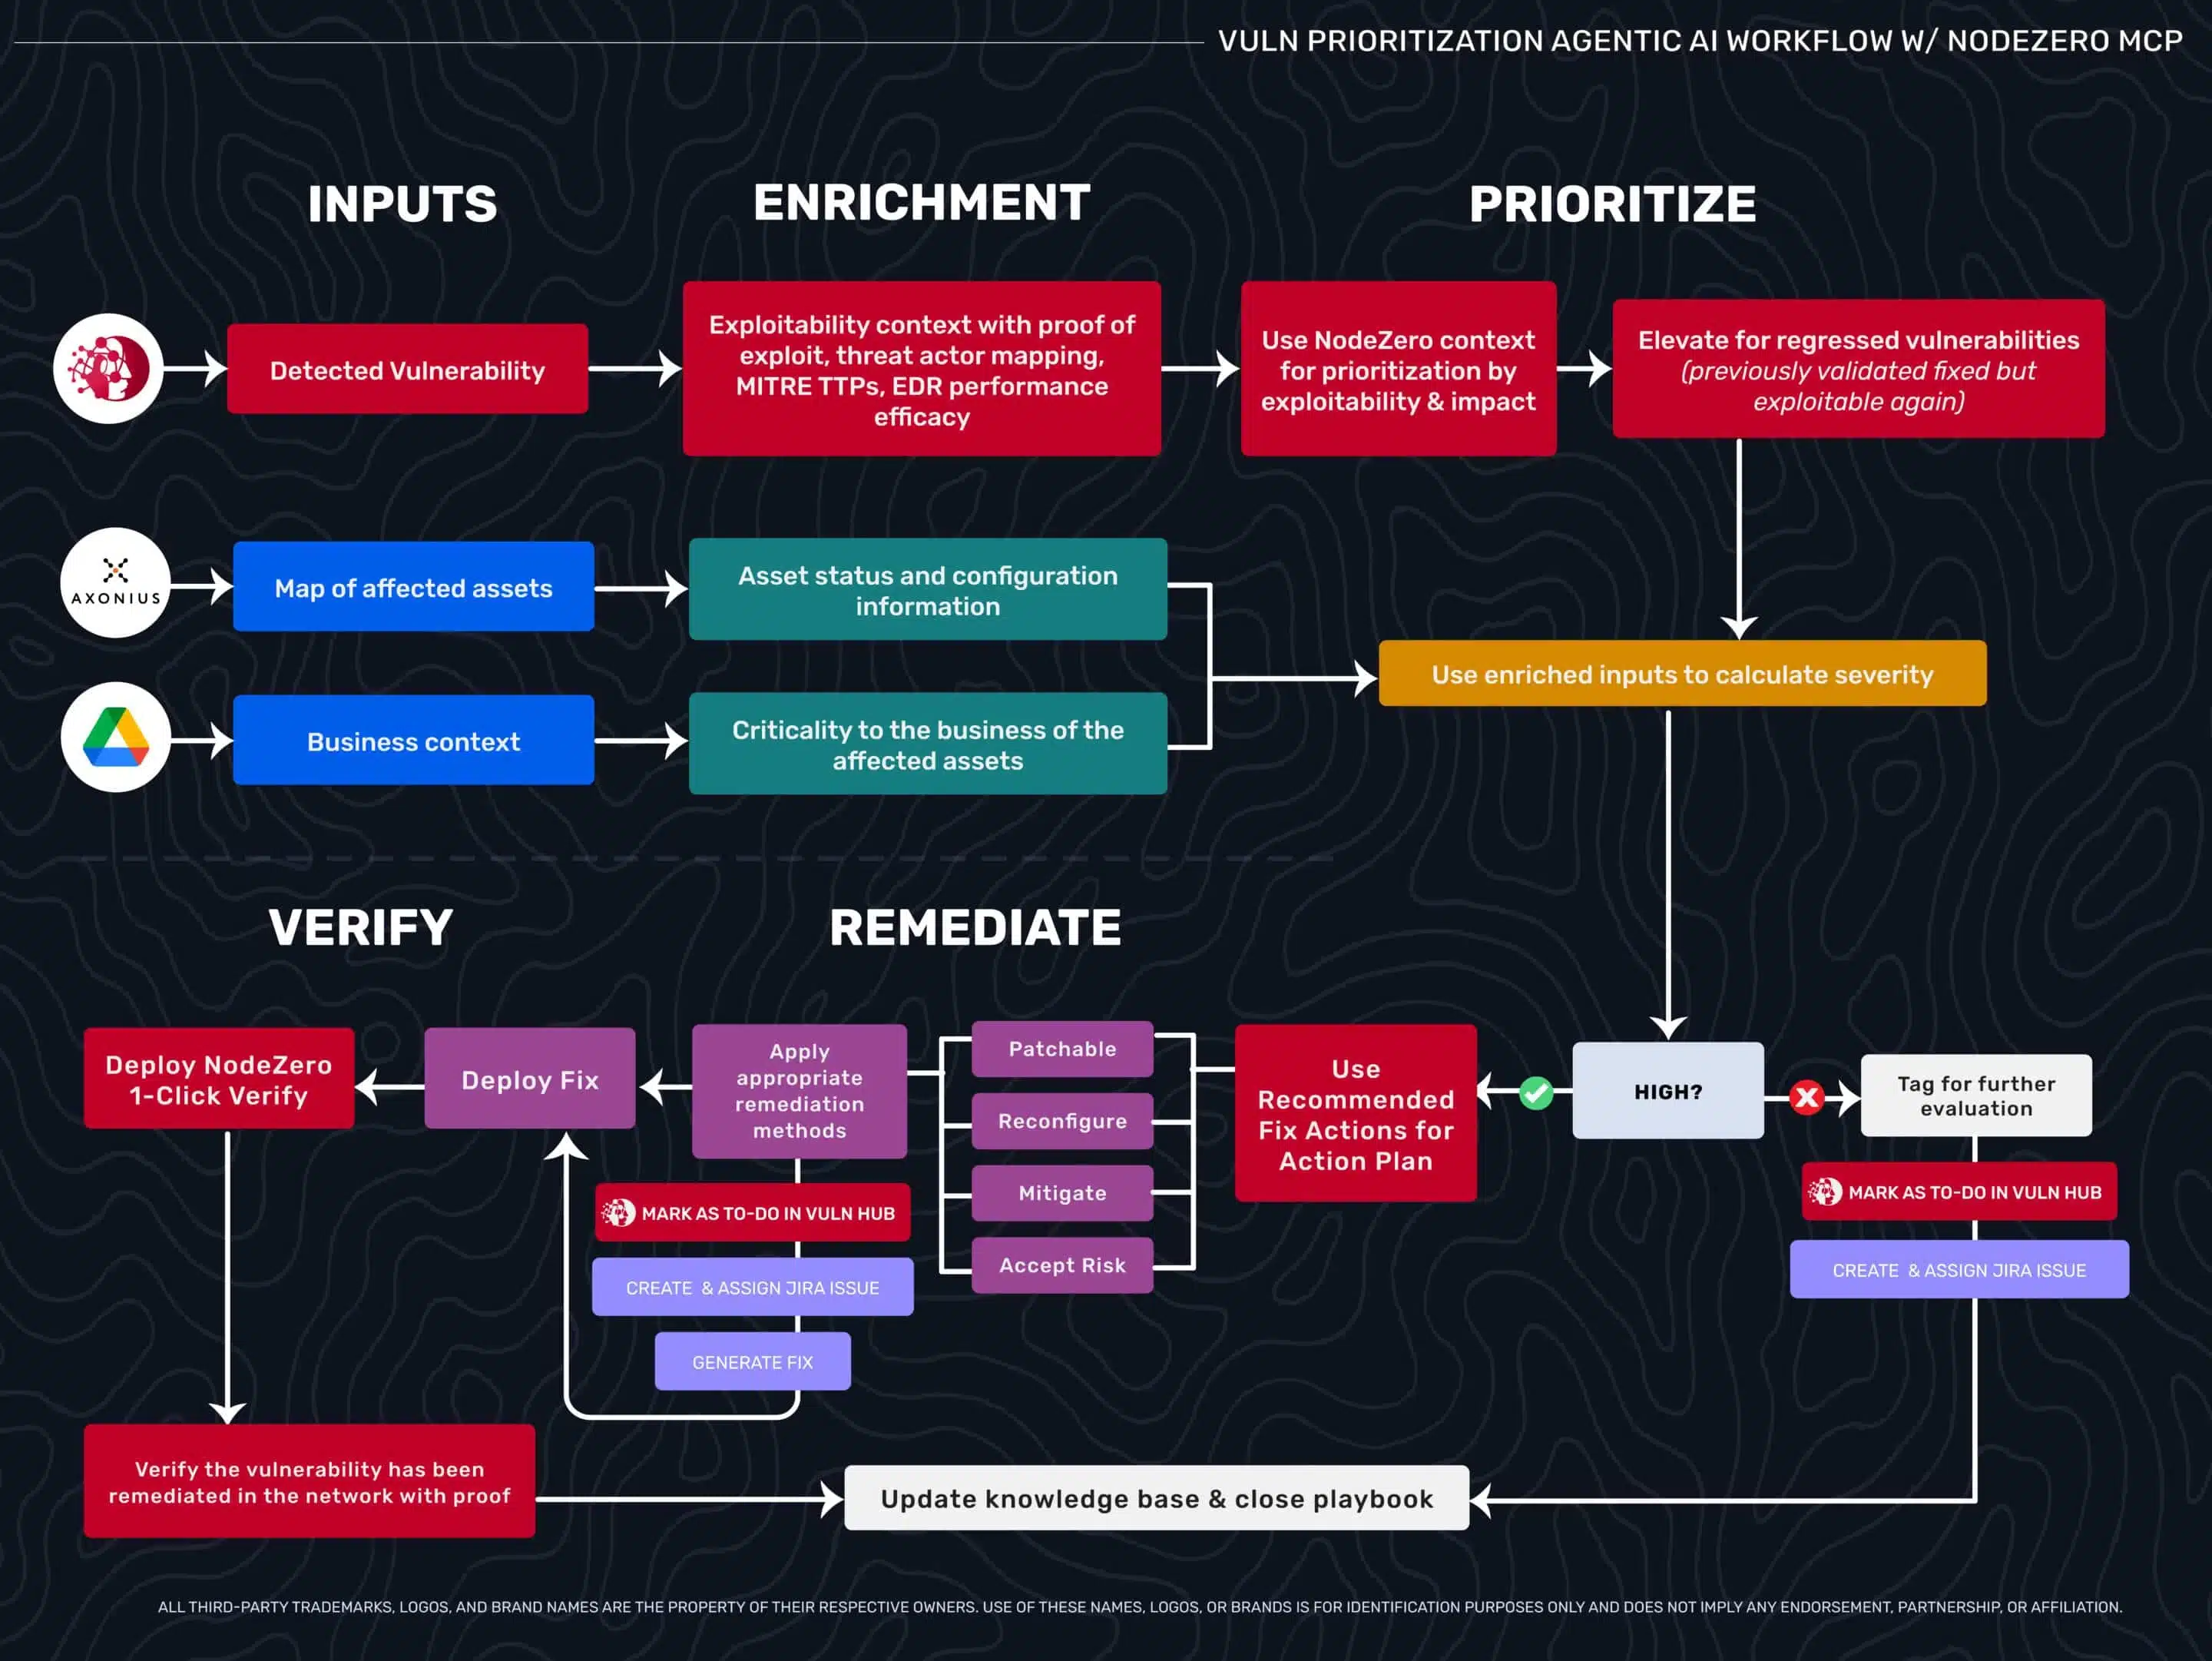
The Quiet Attack Path
October 21, 2025
Attackers turn native Active Directory features into a low-noise, high-impact playbook: stealthy enumeration, Kerberoasting, and AS-REP roasting can produce crackable credentials and clear paths to domain admin in minutes. This post walks through the first 15 minutes of an AD intrusion, why traditional SIEM/EDR struggles to detect it, and what defenders must catch early to…

From Patch Tuesday to Pentest Wednesday®: How a Global Chemical Manufacturer De-Risked a $2B Merger
October 15, 2025
When a $2B merger put a global chemical manufacturer’s security to the test, NodeZero® exposed critical identity risks and domain compromise paths in just 35 minutes. What began as a pilot evolved into a global Pentest Wednesday® program—turning vulnerability data into proof of resilience across 20 sites and thousands of endpoints.

CVE-2025-11371
October 14, 2025
Gladinet CentreStack / Triofox Local File Inclusion (LFI) | 0-Day Active Exploitation
CVE-2025-20362 · CVE-2025-20333 · CVE-2025-20363
October 9, 2025
Cisco ASA / FTD WebVPN Vulnerabilities
CVE-2025-49844
October 9, 2025
Redis Lua Use-After-Free Vulnerability | Critical RCE Risk