Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-114924 and CVE-2026-114925 are critical Oracle E-Business Suite vulnerabilities that, chained, let a remote attacker with no credentials run operating system commands on the application tier over HTTP.
Read More →CVE-2026-132165 is a critical remote code execution vulnerability in the Drupal core installer. Under specific conditions, an unauthenticated attacker can reach install.php and attempt to reinstall a running site.
Read More →Featured
WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
CVE-2026-114924 / CVE-2026-114925
November 19, 2026
CVE-2026-114924 and CVE-2026-114925 are critical Oracle E-Business Suite vulnerabilities that, chained, let a remote attacker with no credentials run operating system commands on the application tier over HTTP.

CVE-2026-132165
November 19, 2026
CVE-2026-132165 is a critical remote code execution vulnerability in the Drupal core installer. Under specific conditions, an unauthenticated attacker can reach install.php and attempt to reinstall a running site.

From Patch Tuesday to Pentest Wednesday®: A CTEM Success Story
The conversation will examine the decisions, obstacles, and lessons behind that work, including how to turn findings into action and sustain progress as environments change. Attendees will leave with practical insights for moving from reporting completed fixes to demonstrating verified reductions in exposure over time.

Machine-Speed Offense Is Here. So Is Machine-Speed Proof.
November 18, 2026
AI shortens the time between a weakness being found and weaponized, but defenders don’t have to wait. See why proof has a shelf life and what real autonomy requires.

CVE-2026-114938
November 17, 2026
CVE-2026-114938, known as Java4Shell, is a high-severity heap buffer overflow in Java's Base64 decoder. Exploitation depends on specific processor, runtime, and application conditions.
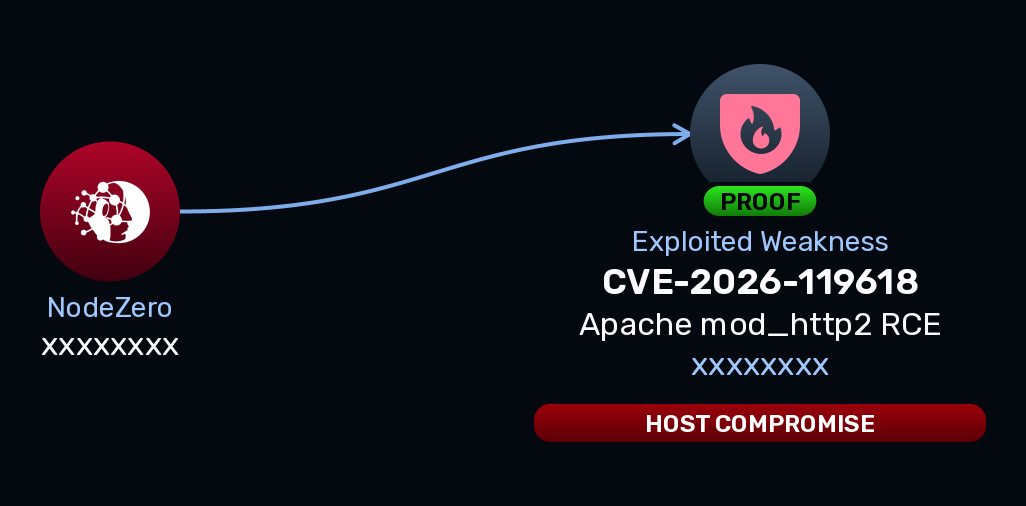
CVE-2026-119618
November 12, 2026
CVE-2026-119618 is a critical race condition in Apache HTTP Server's mod_http2 that can lead to remote code execution without credentials. Fixed in 2.4.71. See affected versions, mitigations, and the NodeZero Rapid Response test.
Does HITL Scale? Human Oversight for Autonomous Security
Explore where human oversight improves autonomous security and where routine approval becomes a bottleneck as agent activity scales. Hear how research, NodeZero's production-safe autonomy, and HITL and HOTL models shape the decisions, staffing, and cost of operating autonomous security continuously.

Stop Patching Blindly: What CISA’s New Prioritization Approach Means for Federal Agencies
November 10, 2026
CISA's BOD 26-04 moves federal agencies from severity-based patching to risk-based prioritization. Here's how validation and verification show which exposures to fix first and prove the fixes worked.
Securing Financial Services: 5 Critical Cybersecurity Advantages of NodeZero
November 9, 2026
Discover 5 key cybersecurity advantages of NodeZero™ for financial services: executive insights, fraud protection, compliance cost reduction, and more.
5 Key Benefits of NodeZero for Enhancing Security in Financial Services Organizations
November 9, 2026
Discover 5 key benefits of NodeZero™ to enhance cybersecurity in financial services. Reduce risk, boost efficiency, and streamline compliance.