Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-76504 is a critical, actively exploited Cisco Catalyst SD-WAN Manager vulnerability that allows unauthenticated API access as the admin user. Horizon3 reverse engineered the flaw, and NodeZero® Rapid Response safely validates exposure.
Read More →CVE-2026-19490 is a critical Citrix NetScaler ADC and Gateway authentication bypass vulnerability included in CISA’s Known Exploited Vulnerabilities catalog. NodeZero® Rapid Response safely validates exposure.
Read More →WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
CVE-2026-76504
September 30, 2026
CVE-2026-76504 is a critical, actively exploited Cisco Catalyst SD-WAN Manager vulnerability that allows unauthenticated API access as the admin user. Horizon3 reverse engineered the flaw, and NodeZero® Rapid Response safely validates exposure.

Horizon3’s Tales from the Trenches: Anthropic’s Mythos and Rejetto HFS
September 30, 2026
Horizon3 researchers used Anthropic’s Mythos to uncover a chain of cryptographic weaknesses in Rejetto HFS, recover a predictable signing key, forge an admin session, and achieve remote code execution.
Your Password Policy Can Pass. Your Passwords Can Still Fail.
See Your Active Directory Passwords From an Attacker’s Perspective Join Horizon3 and Shaun Hunt, CIO of McKenney’s and a longtime NodeZero® customer, for a live conversation about Active Directory password exposure and how NodeZero AD Password Audit helps uncover credentials that could be targeted through password cracking, password spray, credential stuffing, and credential reuse.
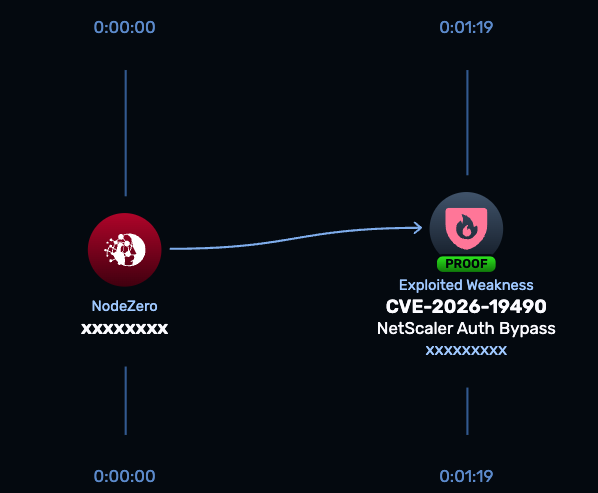
CVE-2026-19490
September 28, 2026
CVE-2026-19490 is a critical Citrix NetScaler ADC and Gateway authentication bypass vulnerability included in CISA’s Known Exploited Vulnerabilities catalog. NodeZero® Rapid Response safely validates exposure.
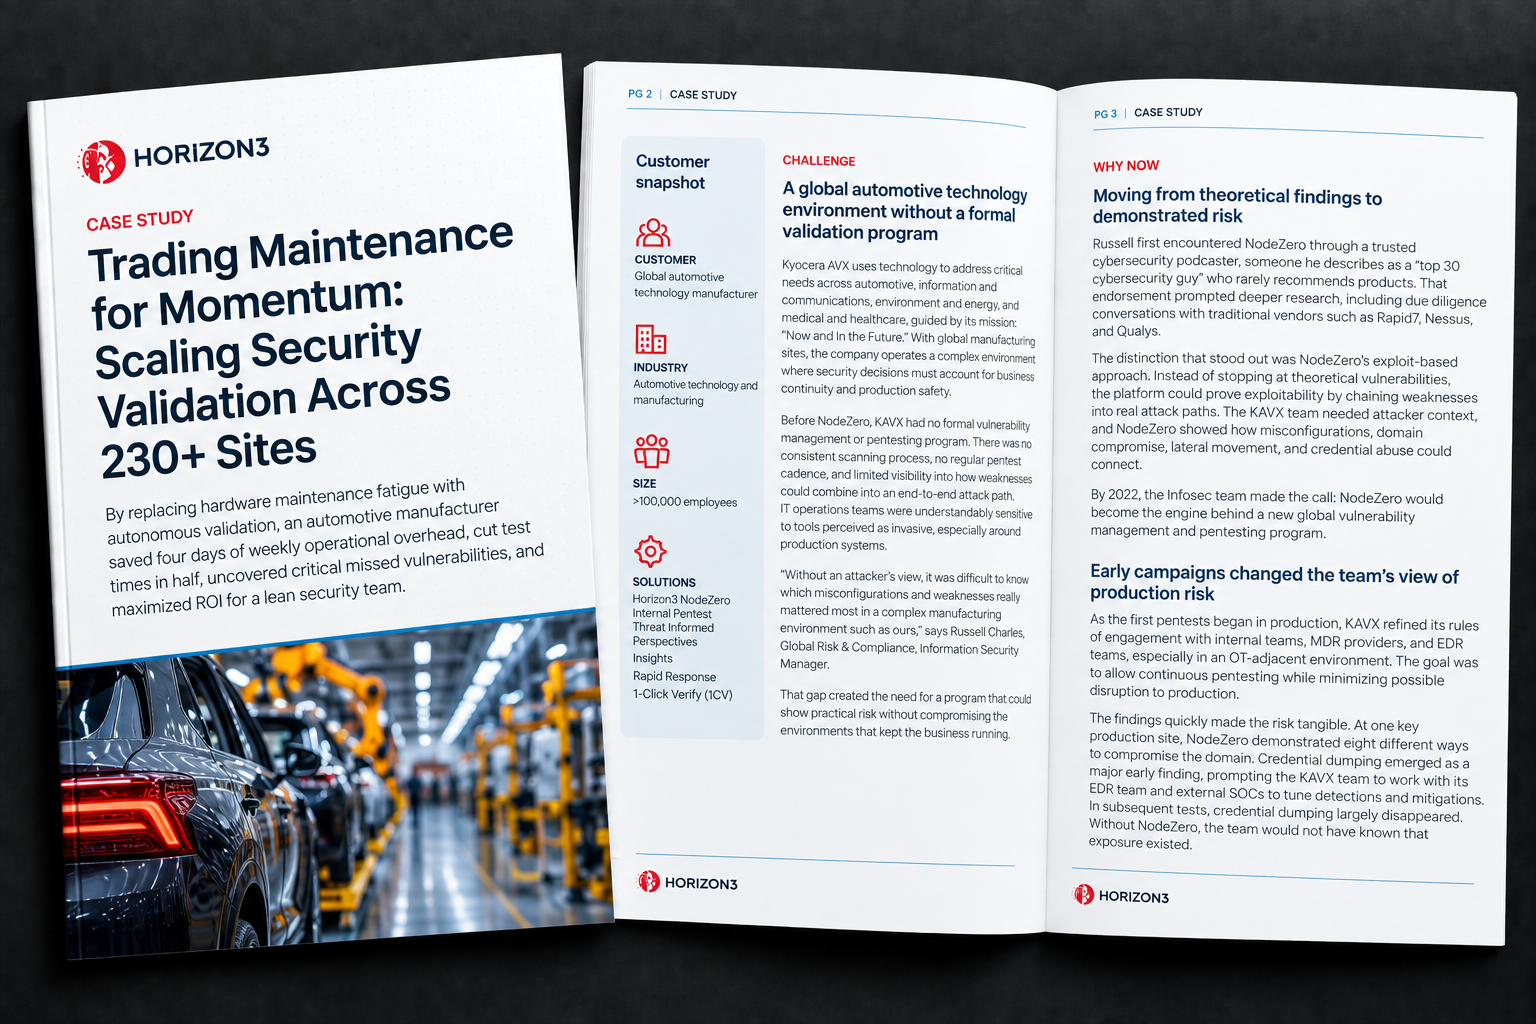
Trading Maintenance for Momentum: Scaling Security Validation Across 230+ Sites
September 25, 2026
See how a global automotive technology manufacturer used NodeZero to reduce testing overhead, cut comparable test runtime by 50%, and scale security validation across more than 230 sites.
Federal & Mission-Critical Security Validation
How federal security teams perform continuous validation — identity-first testing, exploit-led proof, and FedRAMP-aligned remediation with NodeZero Federal™.
NodeZero Federal
September 22, 2026
Horizon3's NodeZero Federal provides production-safe, autonomous penetration testing for federal agencies. Achieve continuous readiness with proven, exploitable findings and rapid retest validation.

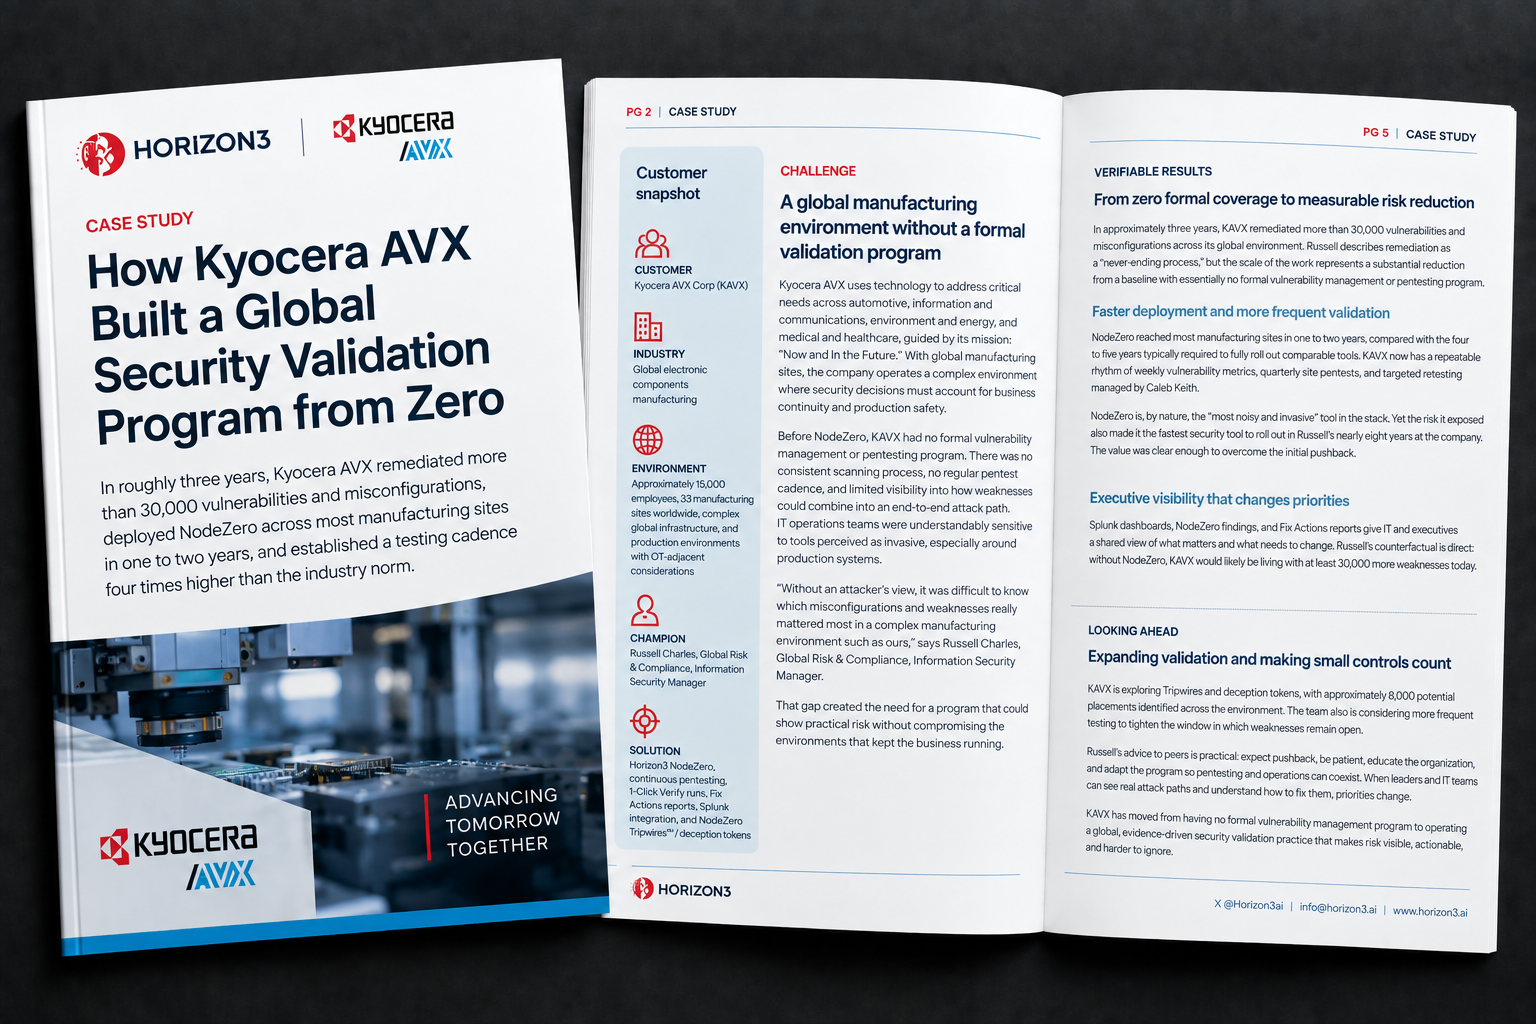
How Kyocera AVX Built a Global Security Validation Program from Zero
September 18, 2026
See how Kyocera AVX used NodeZero to build a global security validation program, scale autonomous pentesting across manufacturing sites, and remediate more than 30,000 vulnerabilities and misconfigurations.
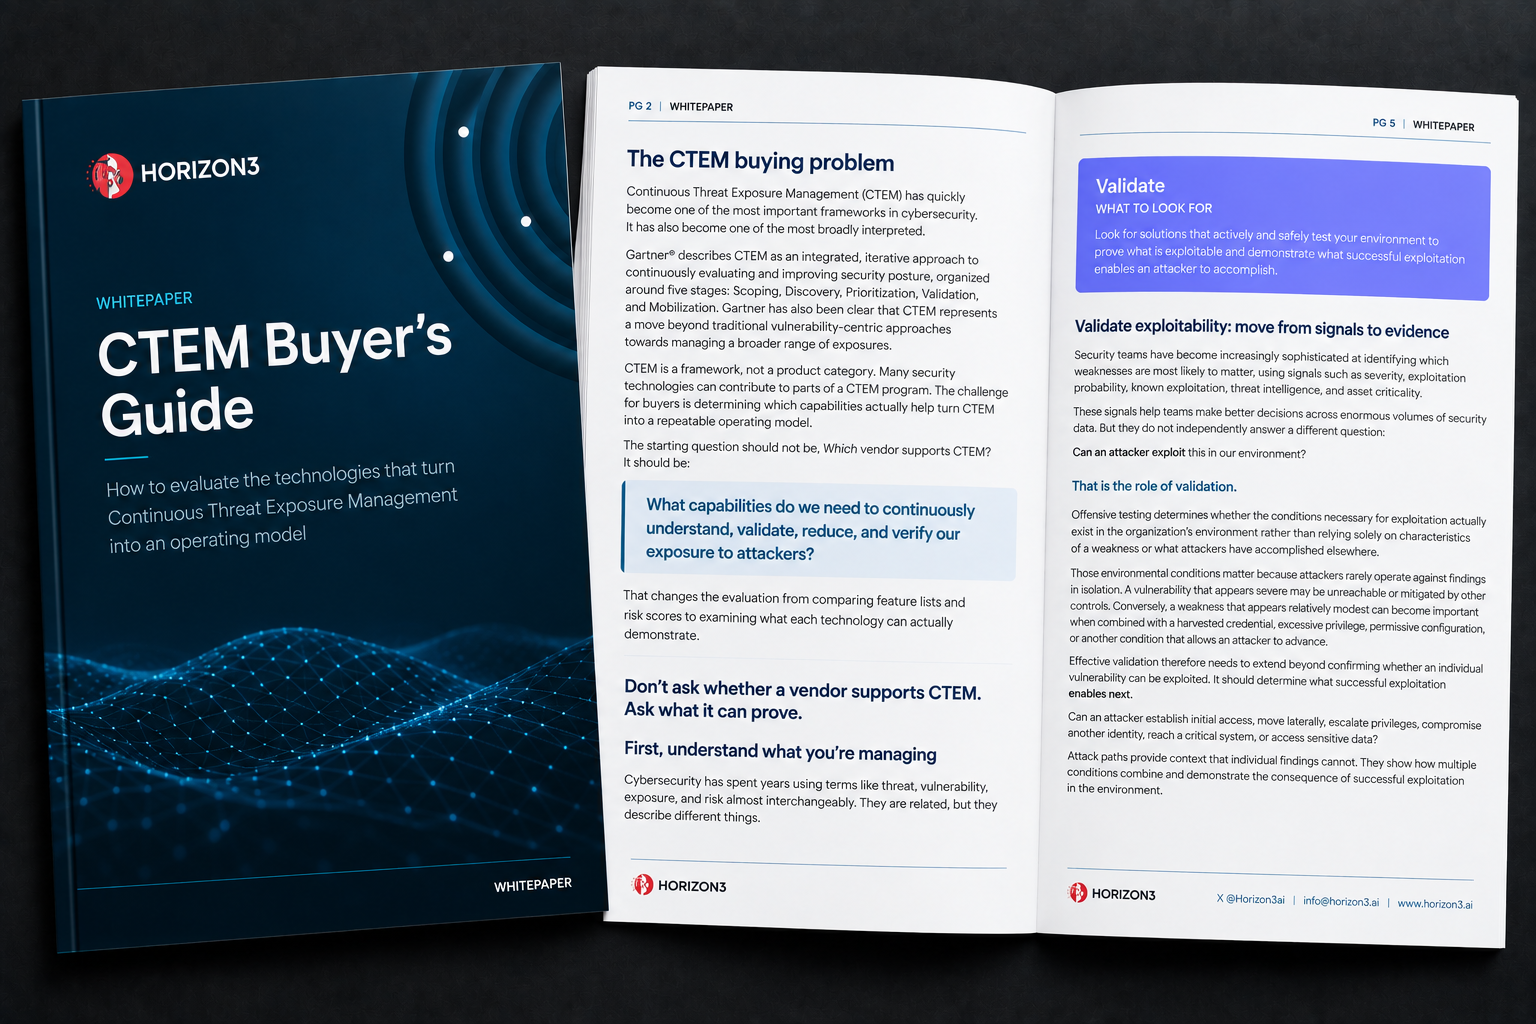
CTEM Buyer’s Guide: How to Evaluate the Technologies That Turn Continuous Threat Exposure Management Into an Operating Model
September 17, 2026
Learn how to evaluate CTEM technologies based on what they can prove, from exploitable attack paths and remediation priorities to verification and measurable risk reduction.
CyberCom 2.0 and the Revolution in AI-Enabled Offensive Cyber Operations
September 17, 2026
AI is transforming the speed, scale, and economics of offensive cyber operations. Explore how CyberCom 2.0 can help lay the foundation for the next era of AI-enabled American cyber power.