Go hack yourself.
Before they do.
Fight AI with AI.
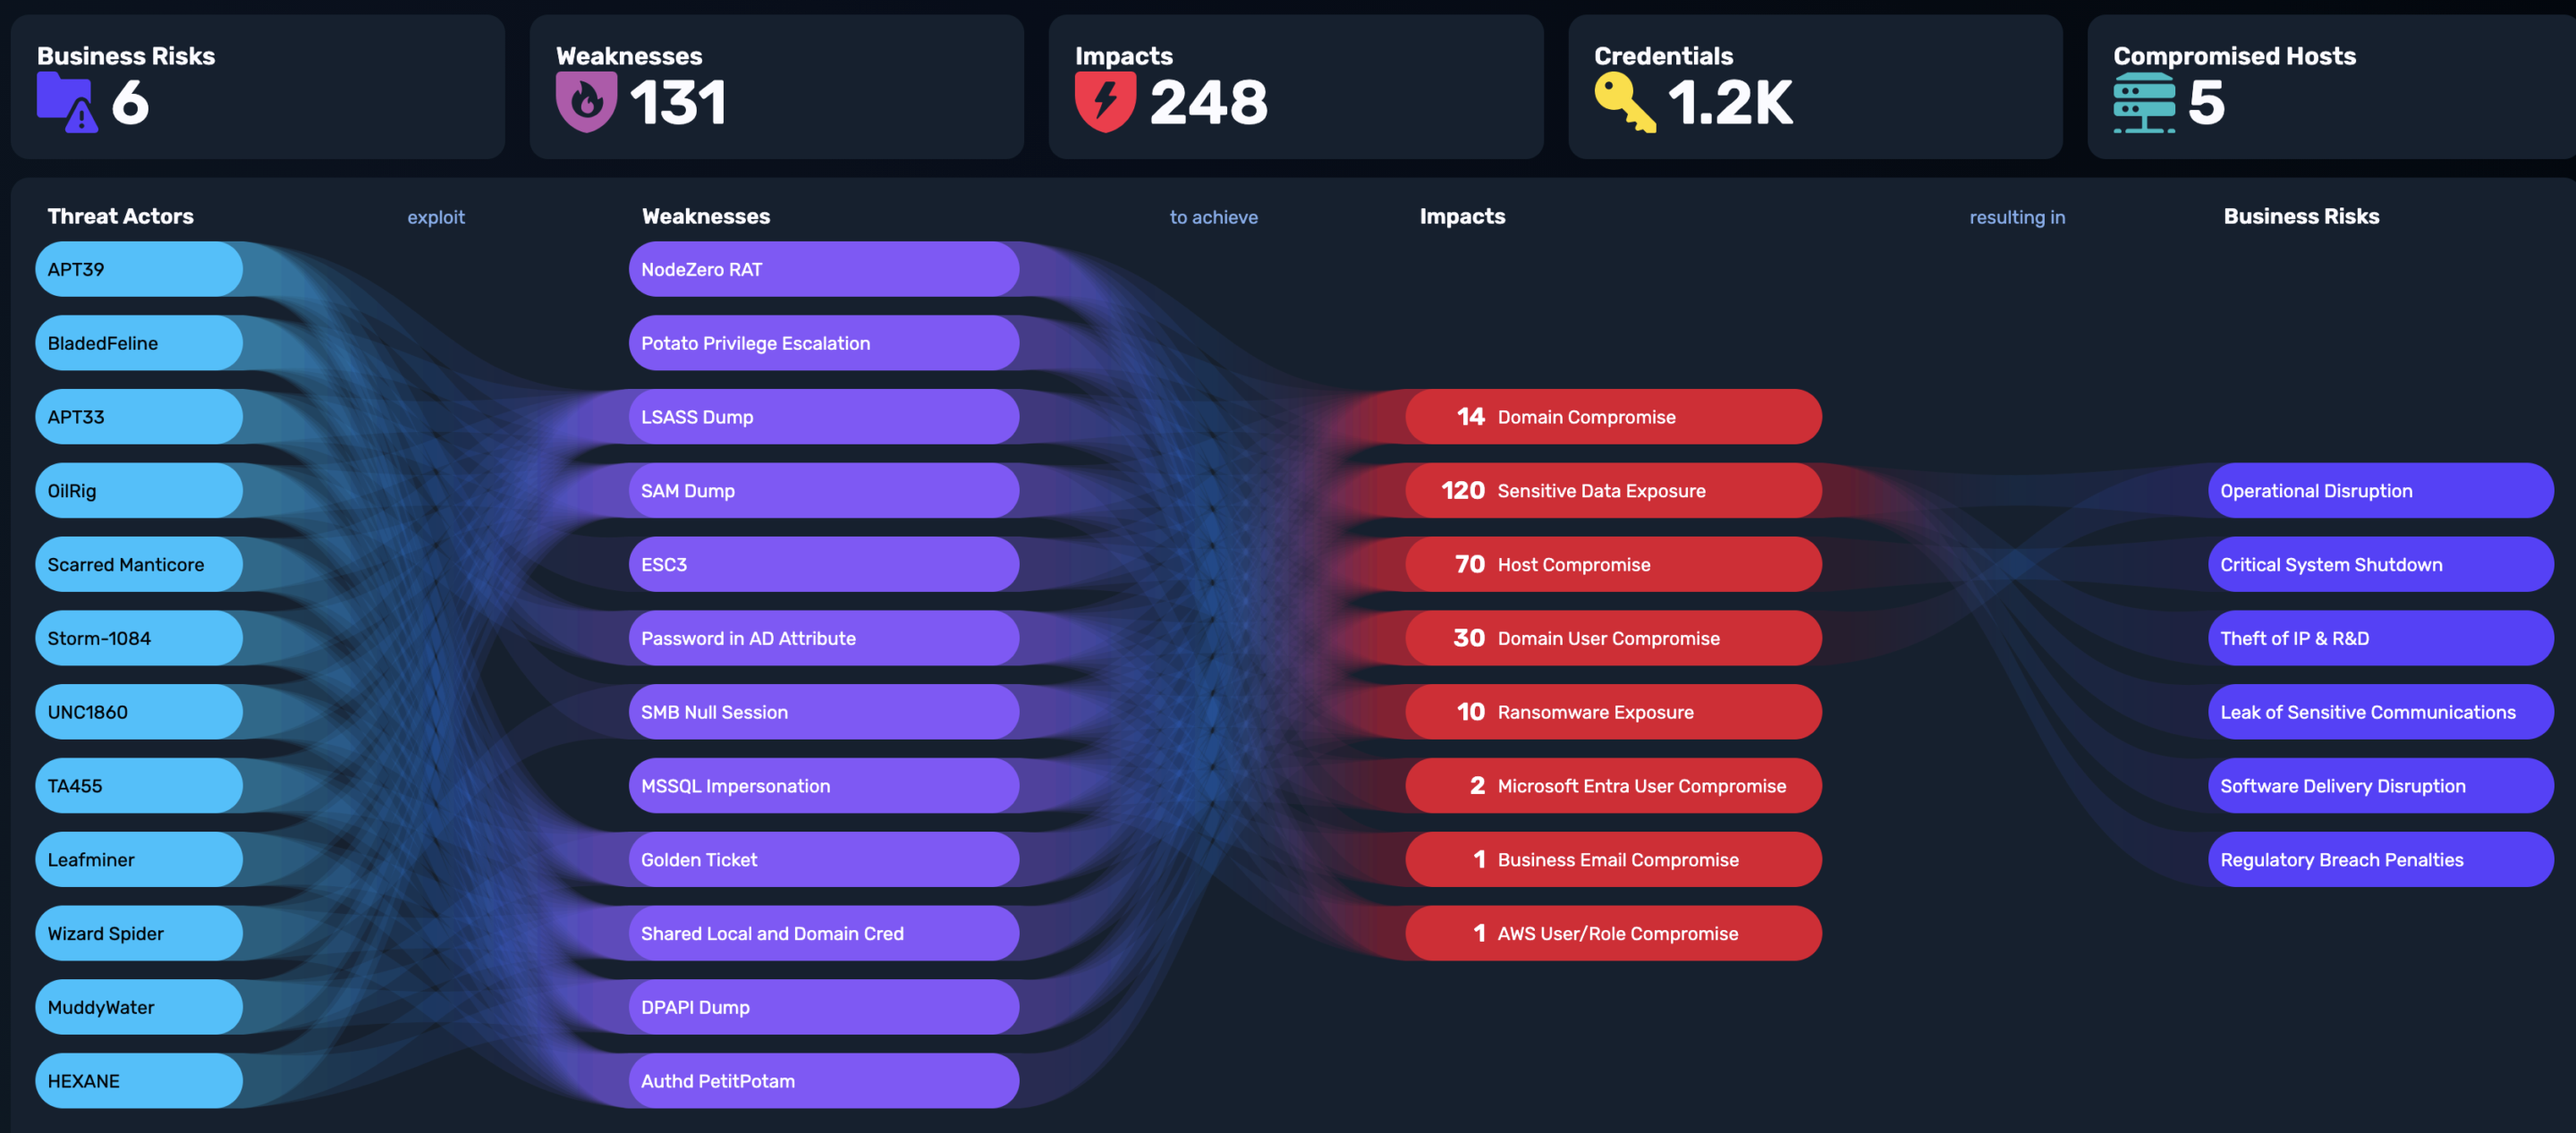
Safely and autonomously hack your production environment, fix what matters most, verify instantly, and repeat continuously. Security you can prove.
Evidence, not opinion.
Don’t just take our word for it.
pentests safely run in production
Horizon3 is trusted by global governments, Fortune 10 giants, and major healthcare providers, where the need for security and safety is absolute.
“…without taking an attacker’s perspective by considering actual attack vectors that they can use to get in, you really can’t be ready.”
Jon Isaacson
Principal Consultant

#1 in Security
Inc. 5000 Fastest Growing Companies

#3 overall
Deloitte Technology Fast 500
#4 in Security
Fast Company’s Most Innovative Companies

Transform Exposure Management
Move from vulnerability management to closing proven attack paths.
Hack
Prove exploitability with real attacks.
Knowing a vulnerability exists isn’t enough. You need to know if it’s actually exploitable.
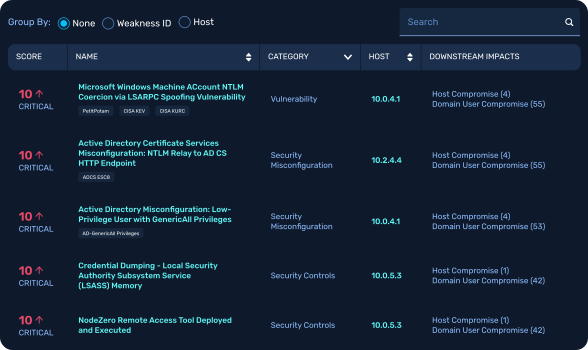
Fix
Prioritize what actually matters.
In an ocean of vulnerabilities, prioritize the ones that are proven to endanger your business.
Verify
Close the loop on every fix.
Don’t just check a box. Re-test to confirm the threat is gone and prove your risk has actually been reduced.
Repeat
Prove continuous resilience.
Your risk changes every time your environment does. Continuously find weaknesses before attackers do — so you stay secure through every change, every day.


Hack
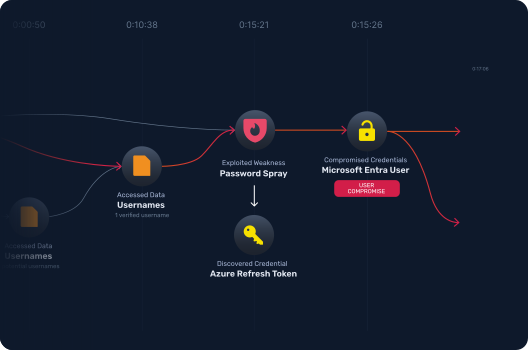
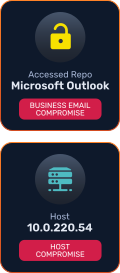
Prove exploitability with real attacks.
Knowing a vulnerability exists isn’t enough. You need to know if it’s actually exploitable.
Fix
Prioritize what actually matters.
Not every vulnerability is worth your time. Prioritize the ones that protect your business.
Verify
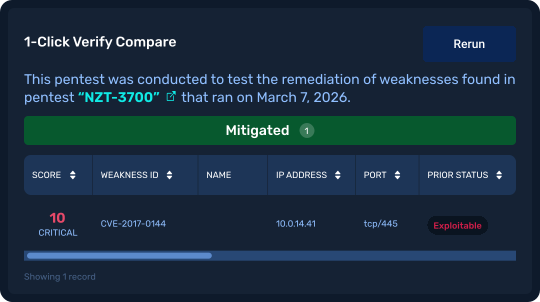
Close the loop on every fix.
Don’t just check a box. Re-test to confirm the threat is gone and prove your risk has actually been reduced.
Repeat
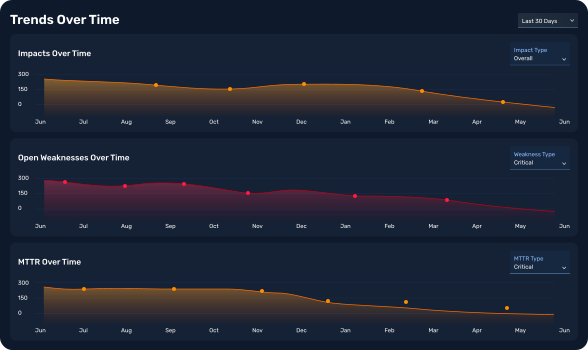
Prove continuous resilience.
Your risk changes every time your environment does. Continuously find weaknesses before attackers do — so you stay secure through every change, every day.
Recommended Reading

Whitepaper
Operationalizing CTEM
Learn how to operationalize CTEM by validating exploitability, prioritizing real risk, verifying fixes, and continuously reducing your attack surface.

Report
The State of Assumed Security
Most organizations measure activity, not resistance. This report reveals where security assumptions break and real exposure begins.

Report
Mythos didn't break cybersecurity
Mythos didn’t create new risk—it exposed how quickly vulnerabilities can become real attack paths.
Proactively prove that you’re resilient.
NodeZero® isn’t a scanner. We show you the real risk and impact on your business. Know exactly where you stand so you can stop guessing and start proving your security posture with confidence.
TRADITIONAL SECURITY
Static pre-defined analysis
Tests what you already know.
Theoretical risk
Delivers opinion-based risk scores.
Paralyzing volume
Produces noisy, high-volume to-do lists that overwhelm your team.
Periodic testing
Delivers results that become stale rapidly.
Based on assumptions
Relies on the hope that your efforts and tools are enough.

Autonomous comprehensive attacks
Learns and adapts with every test.
Proven impact
Real exploitation reveals actual business exposure.
Clarity of action
Gives you confidence on exactly what to fix now, and what can wait.
Continuous validation
Provides continuous proof of your security posture.
Anchored in evidence
Provides continuous proof of your security posture.
Autonomous comprehensive attacks
Learns and adapts with every test.
Proven impact
Real exploitation reveals actual business exposure.
Clarity of action
Gives you confidence on exactly what to fix now, and what can wait.
Continuous validation
Know the impact of every change in your environment.
Anchored in evidence
Provides continuous proof of your security posture.
Static pre-defined analysis
Tests what you already know.
Theoretical risk
Delivers opinion-based risk scores.
Paralyzing volume
Produces noisy, high-volume to-do lists that overwhelm your team.
Periodic testing
Delivers results that become stale rapidly.
Based on assumptions
Relies on the hope that your efforts and tools are enough.