Attack Blogs
SEARCH
CATEGORIES
TAGS
Confluence Server OGNL Injection: CVE-2021-26084
September 13, 2021
On August 25, 2021, Atlassian released a security advisory for CVE-2021-26084, an OGNL injection vulnerability found within a component of Confluence Server and Data Center. This critical vulnerability allows an unauthenticated attacker to execute arbitrary commands on the server. A few days later, on August 31, security researchers @iamnoob and @rootxharsh quickly developed a working proof of concept given the vulnerability…

ProxyShell: More Ways for More Shells
September 4, 2021
In August, Orange Tsai released details and also spoke at BlackHat and DEFCON detailing his security research into Microsoft Exchange. His latest blog post details a series of vulnerabilities dubbed ProxyShell. ProxyShell is a chain of three vulnerabilities: CVE-2021-34473 - Pre-auth Path Confusion leads to ACL Bypass CVE-2021-34523 - Elevation of Privilege on Exchange PowerShell Backend CVE-2021-31207 - Post-auth Arbitrary-File-Write leads to…
Product Updates from our CTO
August 27, 2021
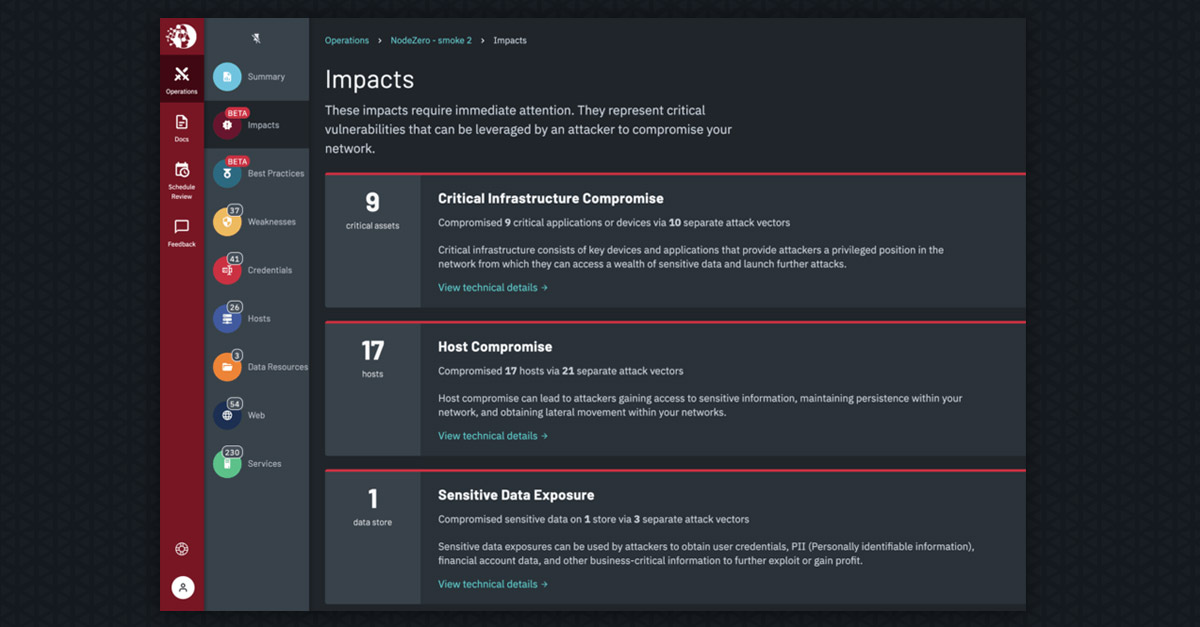
The engineering team has been working tirelessly to improve the "what to wow" user experience, add more attack content, add indicators of best practices and improve analytical insights. Our engineering team focused on these categories based on two observations from customer engagements: About the Author Anthony “Tony P” Pillitiere is the co-founder and Chief Technology…
POC CVE-2021-21972
February 24, 2021
Write the file supplied in the --file argument to the location specified in the --path argument. The file will be written in the context of the vsphere-ui user. If the target is vulnerable, but the exploit fails, it is likely that the vsphere-ui user does not have permissions to write to the specified path.