Nodezero® for financial services
Not every weakness puts financial and insurance services at equal risk.
Financial and insurance institutions face constant vulnerability noise, but the real challenge is knowing which weaknesses create a path to sensitive customer data, payment systems, and core operations. Get board-ready proof of how attackers can reach those systems, and clear evidence that your fixes closed the path.
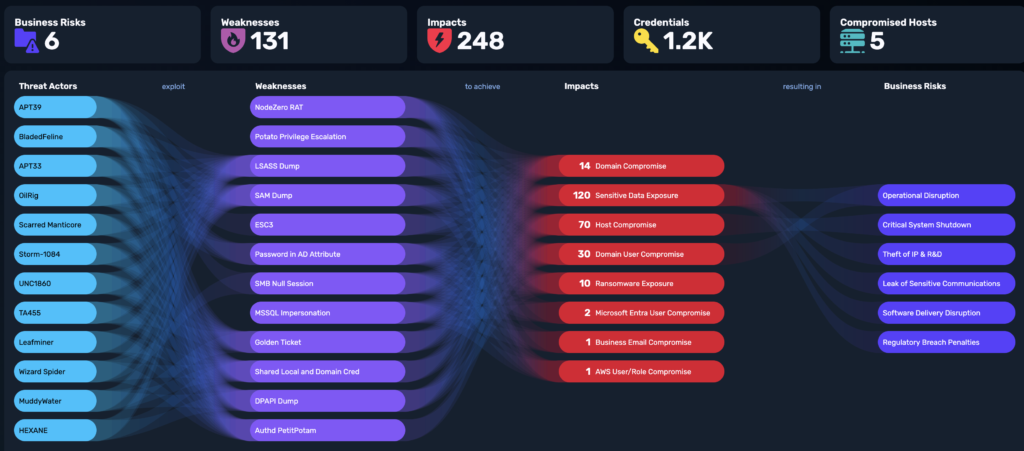
Node zero®. Real results.
Attacker-validated evidence trusted by leading financial and insurance organizations.
See how financial institutions use NodeZero to uncover hidden attack paths, eliminate high-value risk, and replace annual pentests with continuous validation.
GLOBAL INVESTMENT FIRM
251 critical impacts reduced to zero
A lean security team expanded validation across 18 branch locations, eliminating 52 compromised credentials and 67 compromised hosts.
FINANCIAL SERVICES SECURITY PROGRAM
Shifted from annual testing to quarterly validation
A major financial institution ran repeatable testing across 50+ networks, improving audit evidence and insurer confidence.
Large U.S. Insurer
Uncovered 266 cracked passwords
A large insurer uncovered 266 cracked passwords, including 146 accounts sharing the same password,with a confirmed Dev-to-Production path via a compromised Domain Admin service account.
Outcomes drawn from published Horizon3 customer case studies. Individual results vary by environment scope.
On-Demand Webinar
Decoding the ECB’s AI Cyber Mandate for Banks
In this session, you’ll learn how to focus on exploitable risk, where active defense and deception fit, and how to generate the evidence that proves your resilience against AI-driven attacks.
Featured speakers
Yves Mersch
Former Member, ECB Executive Board, ECB (2012–2020)
Frédéric Nakhlé
Director Solution Architect EMEA, Horizon3
Daniel Bird
Field Chief Tech Officer, Horizon3
AJ Nurcombe
Senior Sales Engineer, Horizon3
THE SECURITY VALIDATION WORKFLOW
Find. Fix. Verify. Repeat.
Financial networks change daily. NodeZero gives security teams a continuous, safe way to test what attackers can reach—and prove remediation to auditors and board members.
FIND
Prove exploitability with real attacks.
Knowing a vulnerability exists isn’t enough. You need to know if it’s actually exploitable.
FIX
Prioritize what actually matters.
In an ocean of vulnerabilities, prioritize the ones that are proven to endanger your business.
VERIFY
Close the loop on every fix.
Don’t just check a box. Re-test to confirm the threat is gone and prove your risk has actually been reduced.
REPEAT
Prove continuous resilience.
Your risk changes every time your environment does. Continuously find weaknesses before attackers do—so you stay secure through every change, every day.
Key Capabilities
Built for financial services security teams
Deliver actionable remediation steps to engineers, measurable risk trends to executive leadership, and verifiable proof of control effectiveness to regulators.

Validate control resilience
Test EDR, network segmentation, and IAM controls continuously as production environments change.

Accelerate remediation
Direct engineering teams to the specific root causes breaking full attack chains.

Streamline compliance
Generate reusable evidence to support DORA, PCI DSS, GLBA, FFIEC, and NAIC Insurance Data Security Model Law conversations.

Reduce Cyber Insurance Costs
Provide underwriters with verified proof of posture improvements to support policy renewals.
Build an evidence-based security program
regulatory guidance
DORA & PCI DSS Compliance
Understand how the NodeZero platform helps you meet pentesting requirements with our certified experts.
Infographic
5 Key Benefits of NodeZero for Enhancing Security in Financial Services
How autonomous security testing empowers financial organizations to proactively manage risk, ensure compliance and enhance operational efficiency.
Whitepaper
Meeting the ECB’s AI-Enabled Recommendations
See how Horizon3 maps NodeZero capabilities to each of the ECB’s six cybersecurity focus areas.
SEE NODEZERO IN ACTION
Know what attackers can exploit before they do.
Book a 1:1 conversation on continuously validating your network, prioritizing real risk, and verifying remediation.